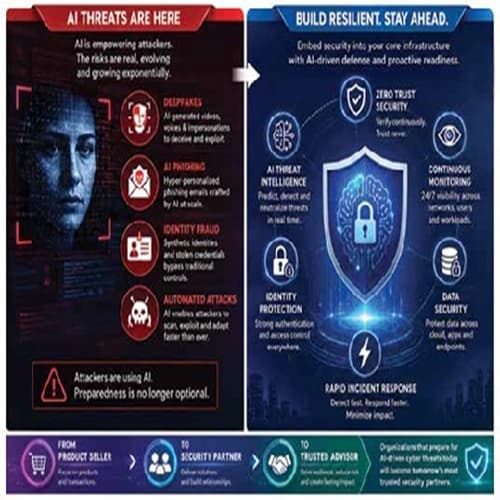
Artificial Intelligence is rapidly transforming the cybersecurity landscape, creating unprecedented opportunities for innovation while simultaneously empowering cybercriminals with more sophisticated attack capabilities. From AI-generated deepfakes and identity fraud to automated phishing campaigns and advanced social engineering, organisations are facing a new generation of threats that traditional perimeter-based security models can no longer adequately address. As enterprises accelerate digital transformation and AI adoption, cybersecurity is evolving from a technology function into a strategic business priority focused on resilience, governance, and continuity.
Against this backdrop, the role of channel partners, value-added distributors, system integrators, and managed security providers is undergoing a significant transformation. Customers are increasingly looking beyond standalone security products and expecting trusted advisors who can help architect secure-by-design digital environments, strengthen cyber resilience, and align security investments with broader business objectives. This shift has prompted technology partners to move from transactional product sales to consultative engagements centred on risk management, Zero Trust architectures, identity protection, AI-powered threat detection, continuous monitoring, and rapid incident response.
To understand how the channel ecosystem is responding to this evolving threat landscape, VARINDIA spoke to leading industry executives from across the cybersecurity value chain. They shared their perspectives on embedding security into core infrastructure, developing capabilities to counter AI-driven threats before they disrupt business operations, and preparing their teams to become strategic advisors in AI security and cyber resilience. Their insights point to a clear industry shift: in the AI era, cyber resilience is being redefined as a core business capability— embedded into architecture, governance, and every stage of an organisation's digital journey.
---------------------------------------------------------------------------------------------------------------
Deep multi-vendor alliances help us build advisory practices around cyber resilience
 PRANAV PARIKH
CTO, UNIFIED DATA-TECH SOLUTIONS LTD.
“We are evolving from an infrastructure reseller to a Secure Infrastructure Partner, transitioning from a traditional product sale-resale model to strategic roadmap-based conversations for securing hybrid work environments where identity, cloud, networking, and AI workloads are integrated into a unified architecture. Our deep multi-vendor alliances with leading OEMs, including Fortinet, Palo Alto, and Check Point, help us build advisory practices around cyber resilience. By positioning network and security convergences powered by a single OS, custom-built ASIC acceleration, SASE, AI-native threat protection, and Zero Trust policies, we help customers integrate these technologies into a cohesive architecture, reduce cyber risk, and participate in long-term managed services contracts.
Our approach is to help organisations build AI-resilient digital infrastructure where identities, applications, cloud platforms, AI workloads, and data are protected by design while positioning ourselves as a trusted advisor on cyber resilience. Identity protection through MFA, Privileged Access Management (PAM), and Zero Trust helps prevent identity compromise, while AI-driven behavioural analysis, UEBA, XDR, and SIEM enable early detection and rapid response. Immutable backups, ransomware protection, cyber vaults, and clean recovery using Cohesity, Commvault, and Veeam strengthen cyber resilience and data protection, complemented by executive awareness programmes, AI phishing simulations, and awareness training.
As customers increasingly prioritise strategic risk management over product-centric purchasing, our approach focuses on understanding business risks rather than individual technology products. Our teams assess and integrate security across identity, cloud, network, applications, AI workloads, and data protection from the design stage, while continuous technical certifications, OEM training, and threat briefings help us stay ahead.
Our mission is simple: make AI trusted, governed and secure by design
 ADIT SHAH
SENIOR PROJECT MANAGER, ADIT MICROSYS PVT. LTD.
“Generative AI is transforming how enterprises operate. But with every AI tool, plugin, and integration adopted, the attack surface grows—often without visibility, governance, or protection. Our vision is to enable secure, sovereign, and compliant AI adoption for every organization, regardless of regulatory, security, or operational constraints. We believe organizations should be able to adopt AI while maintaining the governance, security, and compliance required to operate with confidence.
To identify and mitigate AI-driven threats such as deepfakes, identity fraud, and advanced social engineering attacks before they impact business operations, Adit Microsys is proud to announce our Premier Partnership with Defenix, the enterprise AI Security and Private AI platform delivering the DefenGPT suite to organizations worldwide. Through the DefenGPT AI Security Platform and DefenGPT Private AI, we empower organizations to maintain control over their data, AI models, governance frameworks, and compliance obligations across connected, isolated, and fully air-gapped environments. Our mission is simple: make AI trusted, governed, and secure by design.
As customers increasingly prioritize strategic risk management over product-centric purchasing, we equip our teams to become trusted advisors in AI security and cyber resilience through practical, role-based upskilling. This includes hands-on training for SOC analysts using AI-enabled detection, mastering frameworks such as the OWASP LLM Top 10, applying guardrails using tools like AWS Bedrock, and learning through OEM training pathways, webinars, and industry seminars to counter emerging AI-enabled security threats.”
Our focus is on building secure-by-design, resilient digital infrastructures
 AMARNATH SHETTY
MANAGING DIRECTOR, LDS INFOTECH PVT. LTD.
“The cybersecurity landscape has shifted from perimeter protection to holistic cyber resilience. At LDS Infotech, we are helping customers adopt a secure-by-design approach by integrating security across cloud environments, endpoints, identities, applications, and data. Our focus is on Zero Trust architecture, continuous monitoring, vulnerability management, and proactive threat detection. Rather than deploying standalone security products, we work with customers to build resilient digital infrastructures where security is embedded into every layer of their technology ecosystem.
AI-powered threats are becoming increasingly sophisticated and difficult to detect through conventional methods. To address this challenge, we leverage advanced EDR/XDR, MDR, identity security, threat intelligence, and behavioral analytics solutions that can identify anomalies and suspicious activities in real time. We also emphasize cyber awareness programs and phishing simulation exercises to strengthen the human layer of defense. By combining AI-driven detection capabilities with proactive monitoring and rapid incident response, we help organizations minimize the impact of emerging AI-enabled attacks. Today's customers seek strategic guidance rather than product recommendations. We are investing in continuous training, industry certifications, security assessments, and business-focused consulting skills to enable our teams to engage at a strategic level. Our approach begins with understanding a customer's business objectives, compliance requirements, and risk profile before recommending solutions. This consultative mindset allows our teams to serve as trusted advisors, helping organizations align cybersecurity investments with business resilience, governance, and long-term growth objectives.”
Security must be a foundational business enabler rather than a reactive control
 DEBRAJ DAM
CO-FOUNDER AND CHIEF - VAD VENTURE, SUPERTRON ELECTRONICS (SEPL)
“At SEPL, we have evolved from a product-centric approach to a security-first advisory model. While traditional firewalls remain important, modern cyber resilience requires security to be embedded across the entire IT lifecycle. Consequently, we help customers implement secure-by-design architectures through identity and access management, endpoint security, cloud security, backup and disaster recovery, continuous monitoring, vulnerability assessments, and compliance-driven security frameworks. Our objective is to ensure that security becomes a foundational business enabler rather than a reactive control.
AI-powered attacks are becoming more sophisticated and difficult to detect. To address these risks, we haveexpanded our focus beyond traditional security controls to include advanced threat detection, multi-factor authentication, privileged access controls, email security, endpoint protection, user awareness programs, and incident response readiness. We work closely with leading technology partners to help customers identify anomalous behaviour, mitigate identity-based attacks, and strengthen defences against phishing, deepfakes, and AI-enabled social engineering. Continuous monitoring and proactive risk assessment are essential for detecting anomalies, validating trust, and minimising organisational risk. Today, customers expect business outcomes, not just technology products. Hence, we are continuously investing in technical certifications, cybersecurity training, solution consulting, and industry best practices to strengthen our team’s advisory capabilities. Our approach focuses on understanding business risks, aligning security strategies with organisational goals, and providing long-term guidance on cyber resilience. By combining technology expertise with our advisory capabilities, we help customers make informed decisions and navigate the rapidly evolving AI-driven threat landscape.”
Security is a foundational business commitment, not a purchase decision
 DR. MUKUL GUPTA
DIRECTOR, BM INFOTRADE PVT. LTD.
“We’ve moved well beyond selling firewalls. Over 29 years, BM Infotrade has evolved into a security architecture partner, embedding protection at the infrastructure design stage, not after deployment. Every cloud migration and network build begins with a Zero Trust-first conversation. Our integrated stack—SOC, SIEM, VAPT, WAF, and DLP—isn’t a product menu; it’s a resilience framework tailored to each customer’s environment. Security is no longer a purchase decision for our clients. It’s a foundational business commitment, and we architect it that way from day one.
AI-powered attacks—deepfakes, synthetic identity fraud, and hyper-personalized phishing—are already targeting Indian businesses. Our 24x7 SOC, powered by AI-driven analytics and IBM QRadar SIEM, enables behavioral threat detection that identifies anomalies before they escalate. Our EDR/XDR capabilities monitor endpoints in real time, while identity governance and MFA controls neutralize credential-based attacks. We complement technology with structured employee awareness programs because social engineering exploits people, not just systems. Combined with DPDPA and ISO 27001 compliance advisory, we provide a complete, forward-looking defense against AI-era threats.
The conversation has shifted from “which product?” to “what’s our risk?”, and our teams are built for exactly that. We continuously invest in certifications like CISA and ISO 27001 while fostering a culture of knowledge transfer. Every client engagement starts with a free security consultation and risk-mapping exercise, not a pitch. As an MSSP and System Integrator, we position ourselves as long-term cyber resilience partners, helping CISOs and business leaders frame security decisions in the language of business impact.”
Cyber resilience begins with a security-first architecture

“The threat landscape has evolved far beyond traditional perimeter security. At Arrow PC Network, we are helping customers adopt a security-first architecture where identity, access control, data protection, endpoint security, and continuous monitoring are embedded into the infrastructure from the outset. Our focus is on building cyber resilience through Zero Trust principles, proactive threat visibility, and secure- by-design frameworks that strengthen security across on-premises, cloud, and hybrid environments, enabling organisations to build stronger security foundations from the very beginning.
AI-powered threats are becoming more sophisticated and harder to detect through conventional methods. We are addressing this through a combination of identity verification frameworks, multi-factor authentication, behavioral analytics, threat intelligence, and continuous monitoring. Equally important is user awareness, as many AI-driven attacks target human trust rather than technical vulnerabilities. Our approach focuses on early detection, rapid response, and reducing the attack surface before threats can impact business operations, while helping organisations strengthen overall cyber preparedness.
Customers today expect guidance, not just products. We are continuously investing in workforce readiness through cybersecurity training, AI security awareness, and solution-led consulting capabilities. Our teams are encouraged to understand business risk, compliance requirements, and long-term resilience strategies alongside technology. This enables us to have meaningful conversations with customers around risk management, cyber preparedness, and secure digital transformation, helping us evolve from technology providers into long- term strategic advisors focused on long-term cyber resilience.”
Security has to be embedded into the architecture itself from the outset
 HARIKRISHNA PRABHU
COO, TECHNOBIND SOLUTIONS
“The security conversation has moved far beyond the perimeter. Today, enterprises need protection built into their data, identities, applications, APIs, and cloud environments from the outset. As organizations embrace AI, cloud-native applications, and hybrid infrastructure, security has to be embedded into the architecture itself rather than added as a layer afterwards. At TechnoBind, we are helping partners build resilience around data, identities, APIs, and recovery capabilities. Customers are increasingly asking not only how to prevent an attack, but how quickly they can recover from one, driving demand for integrated cyber resilience frameworks combining prevention, detection, recovery, and governance.
AI has dramatically lowered the barrier for cybercriminals to launch highly convincing attacks at scale.
What makes these threats dangerous is not just the technology behind them, but their ability to exploit trust. Our focus is helping organizations establish stronger identity assurance, continuous behavioural monitoring, and data-centric security controls. We are also seeing growing adoption of AI-powered analytics to identify anomalies that traditional rule-based systems miss. The key is moving from reactive threat detection to continuous risk assessment, where suspicious activity is identified and contained before it disrupts business operations. AI has elevated cybersecurity from a technology challenge to a business governance issue, moving conversations to leadership and board levels. We are equipping our teams and partners beyond product knowledge, focusing on customers’ risk posture, regulatory obligations, AI adoption roadmaps, and cyber recovery requirements. This enables outcome-driven discussions around resilience, business continuity, governance, and actionable security strategies.”
Security is not something added later but designed into infrastructure from the start
 JIGAR SANGHVI
DIRECTOR, SANGHVI INFOTECH PVT. LTD.
“Security is no longer a gate at the perimeter; it is an architectural principle. Our evolution as a system integrator has been from traditional firewall-led protection to embedding secure-by-design resilience into the very DNA of customer infrastructure. Across Wi-Fi, telecom, OFC, surveillance, and edge networks, we now build environments where segmentation, visibility, hardening, secure access, and continuity are engineered from the outset. In an era of distributed operations and rising threat complexity, security is not something added later but designed into infrastructure from the start.
As a system integrator, we have expanded our security approach to address AI-driven threats such as deepfakes, identity fraud, and advanced social engineering attacks. Our capabilities focus on intelligent monitoring, identity verification, anomaly detection, secure access architecture, and rapid response integration across the customer environment. Rather than relying only on perimeter controls, we help build verification-led, resilient infrastructure that detects suspicious behavior, validates authenticity, and contains threats before they impact operations. As customers increasingly prioritize strategic risk management over product-centric purchasing, we are reshaping our teams into advisory-led practitioners focused on AI security and cyber resilience. We are strengthening expertise in governance and risk frameworks and the ability to translate cybersecurity into business-relevant conversations around continuity, trust, compliance, and operational stability. Our objective is to ensure every engagement reflects not only technical knowledge but also a cler understanding of risk posture, resilience priorities and long term strategic impact.
 We build security into the architecture itself, not afterward
KAMAL ZUTSHI
CTO, PROGRESSIVE INFOTECH
“The perimeter has effectively dissolved; hybrid work, multi-cloud, and SaaS mean there is no clean inside to defend. At Progressive Techserve, we build security into the architecture itself. We treat identity as the control plane and apply Zero Trust end-to-end, prioritizing least-privilege access and continuous verification. Secure-by-design means embedding controls at the build stage through threat modelling, secure architecture reviews, and hardened baselines, reinforced with continuous vulnerability management, posture assessment, and monitoring. The result is infrastructure that resists compromise, limits blast radius, and recovers fast, rather than protection bolted on afterward.
AI has raised the realism of attacks; deepfake fraud, synthetic identities, and targeted social engineering defeat conventional controls. Since most breaches exploit human trust, we run AI/ML analytics in a 24x7 SOC with UEBA to flag behavioral deviations, while hardening identity via conditional access and phishing-resistant MFA. On email, we enforce SPF, DKIM, and DMARC with BIMI to block spoofing. A continuous assess–aware–protect–empower loop simulates multi-vector AI threats, scores individual risk, and drives personalized training with automated AI triage for fast containment.
Customers have shifted from asking 'which product should I buy?' to 'how do I manage my risk?' Our role is consultative—we work backward from business risk to the right controls instead of leading with tools. To advise credibly, we ground recommendations in recognized standards like NIST CSF, ISO 27001, MITRE ATT&CK, and the NIST AI RMF. Progressive Techserve supports this with 55+ cybersecurity analysts holding prestigious certifications across CISA, CISM, CISSP, CEH, CCNA, and C|PENT.”
Cyber resilience is a business imperative in the age of AI
 KARTHIK NARAYANAN
DIRECTOR – ADVANCED SOLUTIONS, INGRAM MICRO INDIA
“The cybersecurity conversation has fundamentally shifted from protecting the perimeter to building resilience into the fabric of the enterprise. As organizations accelerate AI adoption, security can no longer be an afterthought; it must be embedded by design across networks, cloud environments, identities, applications, and data. Our focus is on helping partners and customers architect secure digital foundations that are scalable, adaptive, and resilient against evolving threats.
The rise of AI-driven attacks, including deepfakes, identity spoofing, automated phishing, and sophisticated social engineering campaigns, demands a new generation of security capabilities. We are working closely with leading cybersecurity vendors to enable solutions that leverage AI for threat detection, behavioral analytics, identity protection, zero-trust access, and real-time incident response. By combining advanced security technologies with threat intelligence and proactive monitoring, we help organizations identify and mitigate risks before they impact business operations.
At the same time, customers are increasingly seeking strategic guidance rather than standalone products. To address this shift, we are investing significantly in training, solution architecture expertise, cyber resilience workshops, and industry-specific security frameworks. Our objective is to empower our teams and partner ecosystem to engage as trusted advisors, helping customers assess risk, strengthen governance, improve cyber preparedness, and align security investments with business outcomes. In the age of AI, cyber resilience is not just a technology priority; it is a business imperative.”
Cybersecurity should be built into the foundation, not added after deployment
 KUMAR BACHCHAN
MD & CEO, NIVESHAN TECHNOLOGIES INDIA PVT. LTD.
“We believe cybersecurity should be built into the foundation of digital infrastructure rather than added as a layer after deployment. At Niveshan, we have always believed in delivering standalone security products while designing secure-by-design environments where cybersecurity is integrated across data centres, hybrid cloud, enterprise networking, and smart infrastructure. By combining Zero Trust principles, identity and access management, secure network architecture, continuous monitoring, and managed security operations, we help customers build resilient, scalable, future-ready digital ecosystems prepared for evolving cyber threats.
As AI-powered cyber threats continue to evolve, we are strengthening our cybersecurity capabilities with intelligent, proactive defence mechanisms. We leverage AI-driven analytics, SIEM, threat intelligence, and automated incident response to identify abnormal behaviour and respond faster to emerging threats. Combined with continuous vulnerability management, endpoint security, identity protection, and our 24×7 Security Operations Centre (SOC), these capabilities help customers strengthen cyber resilience against increasingly sophisticated AI-driven attacks while improving overall cyber preparedness.
We believe customers today expect strategic partners, not just technology providers. That is why we continue to invest in deep technical expertise through our NTPL Academy, industry certifications, OEM partnerships, and hands-on experience across mission- critical national infrastructure projects. Our teams engage with customers from the consulting stage, understanding business objectives, assessing risks, designing resilient architectures, and providing end-to-end managed security services. This consultative approach enables us to deliver long-term value while helping organizations confidently navigate the rapidly evolving ai driven cybersecurity landscape.
Our approach to cybersecurity is holistic, from audit to implementation
 L ASHOK
MD, FUTURENET TECHNOLOGIES (INDIA) PVT. LTD.
“Our approach is mostly holistic. We believe in addressing the changing landscape strategically from the very beginning rather than just delivering standalone security tools. We start with a detailed audit to thoroughly assess the threat landscape and suggest the appropriate equipments for our customers' specific core requirements, ensuring resilience is considered early.
Our audit framework comprehensively examines the security risk surface which includes AI-driven threats, such as deepfakes, identity fraud, or advanced social engineering attacks. To mitigate these before they impact business operations, the key is a structured user awareness training on the possible threats and leveraging our established training framework to address the human layer.
As customers increasingly prioritize strategic risk management over product-centric purchasing, we focus on deep advisory capabilities. Our consulting framework coupled with implementation capabilities helps us to cater to customers requirements holistically, enabling our teams to serve as trusted partners who translate technology needs into long-term cyber resilience.”
Moving beyond product delivery to build secure, future-ready digital environments
 MINAL BHAGAT
CO-FOUNDER, ENSONIC COMPUTECH PVT. LTD.
“At Ensonic Computech, we believe cybersecurity must be an integral part of every digital transformation initiative. Rather than focusing solely on perimeter security, we promote a secure-by-design approach across smart classrooms, collaboration spaces, AV infrastructure, and digital communication environments. Our deployments emphasize secure device integration, authenticated access, controlled user permissions, and reliable
network practices, helping customers build resilient digital ecosystems from the ground up while supporting
secure and scalable digital transformation initiatives. As AI-driven threats continue to evolve, we focus on proactive security awareness and responsible technology implementation. Our solutions support secure
conferencing, controlled access environments, user authentication, and data protection measures that help minimize risks associated with unauthorized access, identity misuse, and social engineering attacks. We continuously evaluate emerging technologies and industry best practices to strengthen security readiness across customer deployments, enabling customers to adopt evolving technologies with greater confidence while maintaining secure digital environments. We are investing in continuous learning, technical training, and customer-focused engagement programs to strengthen our team's advisory capabilities. By staying updated on AI trends, cybersecurity developments, and digital transformation requirements, our professionals are better equipped to guide customers on secure technology adoption. Our goal is to move beyond product delivery and become a trusted partner, helping organizations build future-ready, resilient, and secure digital environments while delivering long-term value through customer-centric engagement and trusted technology advisory.”
Building a stronger security foundation for evolving technology environments
 JATIN SAWHNEYDIRECTOR,
TEAM COMPUTERS
“The nature of cyber risk has changed significantly. Organizations today operate across on-premises environments, multiple cloud platforms, remote workplaces, and increasingly connected business systems, where security cannot be limited to network boundaries or standalone security products. At Team Computers, we work with customers to incorporate security into the design, deployment, and management of IT infrastructure across cloud environments, data centers, digital workplaces, and enterprise networks. By combining infrastructure expertise with cybersecurity services, identity management, endpoint security, monitoring, and compliance frameworks, we help organizations reduce risk exposure, maintain business continuity, and create a stronger security foundation. AI-driven threats are increasing the speed, scale, and sophistication of attacks.
Deepfakes, impersonation attempts, intelligent phishing campaigns, and identity-based attacks require organizations to look beyond traditional security controls. Our approach focuses on strengthening visibility, verification, and response capabilities through security monitoring, endpoint protection, identity and access management, threat detection, security assessments, and user preparedness through stronger security awareness, authentication controls, and clear response procedures.
Customers are increasingly looking for guidance on how security decisions affect business operations, regulatory requirements, and long-term risk management. We invest in continuous learning across our consulting, infrastructure, cloud, and cybersecurity teams. Through assessments, workshops, architecture reviews, and risk discussions, we combine technical expertise with an understanding of operational requirements to serve as a long-term technology partner and help customers establish practices and frameworks that support resilience in an increasingly complex threat environment.”
Resilience is built in from day one, not added later
 NK MEHTA
MD & CEO, SECURE NETWORK SOLUTIONS INDIA PVT. LTD.
“At SNS, secure by design has been our DNA since inception—not an afterthought but the foundation of every engagement. Whether consulting, implementing, or managing SOC operations, resilience and security drive decision making. In projects involving SD-WAN, WAF, and core network redesign, we balance performance with embedded security principles. By shrinking the attack surface and architecting security into the infrastructure itself, we help customers move beyond reactive defences. This approach ensures resilience is built in from day one, enabling organizations to withstand AI-driven threats while maintaining agility and trust.
SNS continuously invests in advanced defences against AI-powered threats. Our portfolio includes AI
guardrails to prevent misuse, AI audits to uncover hidden risks, and AI-driven penetration testing to simulate evolving attack vectors. We have embedded AI into SOC automation for faster detection of anomalies such as deepfakes and identity fraud. By combining Agentic AI with contextual telemetry, our solutions operate at machine speed to counter sophisticated social engineering before it disrupts business, ensuring customers are protected and prepared for the next wave of AI-accelerated attacks.
For SNS, a consultative approach is the cornerstone of service delivery. Every solution is designed with clear risk reasoning—what it mitigates, what it does not, and the roadmap ahead. Our trained and certified specialists translate complex AI-driven risks into strategic guidance, building customer confidence through resilience-focused decisions. With over 25 years of trust, SNS continues to evolve as a strategic advisor, embedding risk management into design, implementation, and ongoing support.”
Cybersecurity is a business continuity imperative in the AI era
 PANKAJ KUMAR AGARWAL
CEO & MANAGING PARTNER, DOCKET CARE SYSTEMS
“AI is transforming both business innovation and cybercrime. As technology partners, our role has evolved significantly from supplying security products to helping customers build cyber resilience by design. Traditionally, cybersecurity focused on firewalls and perimeter defence. Today, we advocate a secure-by-design approach that integrates security into every layer of IT infrastructure—from endpoints, identity management, cloud workloads, data protection, backup, and network architecture to user awareness. We work closely with customers to assess risks, implement Zero Trust principles, and build resilience against modern attack vectors. AI-driven threats such as deepfakes, identity impersonation, phishing automation, and social engineering attacks require advanced countermeasures. Our focus is on deploying AI-powered threat detection, multi-factor authentication, identity governance, behavioural analytics, security monitoring, and employee awareness programs. We also encourage organisations to adopt continuous risk assessments and incident response planning to detect and contain threats before they impact business operations. Customers today seek trusted advisors rather than product vendors. Accordingly, we continuously upskill our teams through cybersecurity certifications, AI-security awareness programs, vendor-led training, and industry collaboration. Our objective is to help customers understand emerging risks, align security investments with business goals, and develop long-term cyber resilience strategies. In the AI era, cybersecurity is no longer a technology issue alone—it is a business continuity imperative. Organisations that proactively invest in cyber resilience, governance, and AI-enabled security capabilities will be better positioned to earn stakeholder trust and sustain growth in an increasingly complex threat landscape.”
Security must be woven into business, not bolted on as an afterthought
 PRASHANTH SUBRAMANIAN
CO-FOUNDER & DIRECTOR, QUADRASYSTEMS.NET (INDIA) PVT. LTD.
“The perimeter has been irrelevant for years. We stopped selling firewall refresh cycles and started asking a different question: what does your threat surface actually look like, and is security woven into how you operate—or bolted on as an afterthought? Our BluForge Shield advisory practice begins every engagement with a posture and architecture review. We design Zero Trust frameworks from the inside out—identity, access, data and workload—before recommending products. The goal is infrastructure that is inherently resilient, not infrastructure that depends on a perimeter that no longer exists.
AI-driven attacks are winning because they exploit the gap between detection speed and human responsetime. Deepfakes, synthetic identity fraud and AI-generated phishing are engineered to evade signature-based systems. Our response is multi-layered. BluForge Ops and BluForge Pulse run on Microsoft Sentinel and Defender XDR, correlating behavioural signals across identity, endpoint and cloud. Our MITRE ATT&CK-aligned threat hunters proactively surface lateral movement before it escalates, while our Accelerated Intelligence Group embeds AI-powered anomaly detection to flag synthetic or compromised credential behaviour that rule-based systems routinely miss.
Products don't build resilience. Advisors do. We've invested in developing our Cybersecurity Group alongside our Accelerated Intelligence Group because the intersection of AI expertise and security expertise is where the most dangerous gaps live today. Our Threat Doctor framework translates threat intelligence into board-level risk language. The metric that matters isn't tool coverage—it's whether a CISO leaves with a clearer picture of actual risk exposure. That's the difference between a trusted advisor and a vendor.”
Resilience isn’t a product you buy; it’s a property you design into the system
 RAJESH ANANTHAKRISHNAN
PRESIDENT AND HEAD - MANAGED SECURITY SERVICES, INSPIRA ENTERPRISE
“The honest starting point is this: the firewall didn’t disappear—it just stopped being the strategy. We’ve moved from device management to managed cyber resiliency, shifting the customer conversation from product- centric to outcome-driven. Our iSMART2 platform gives customers a continuous view of platform availability and the health of every control we manage, while ServiceNow ITSM and ITOM automate operations with ITIL discipline. We assume compromise and design for it through continuous exposure management, breach- and-attack simulation, an autonomous SOC, secure-by-design for OT aligned to IEC 62443, and measurable SLAs. Resilience isn’t a product you buy. It’s a property you design into the system and operate with discipline every day.
AI has fundamentally changed the economics of deception. We’ve built deepfake, fraud and disinformation detection into our managed services, treating these primarily as identity attacks. Our IAM Centre of Excellence leads conversations around non-human and AI-agent identity, identity threat detection and response, managed privileged access, dark-web monitoring, executive-impersonation alerts and attack-surface management. When ITDR detects anomalous identities, our autonomous SOC orchestrates rapid containment through ServiceNow SecOps and third-party ITDR. Buyers now ask about risk and resilience, not products. We train our teams on frameworks including NIST AI RMF, ISO 42001, OWASP and MITRE ATLAS, supported by our Cyber for AI framework. Combined with AI Control Tower, AI risk-and-readiness assessments and our co-managed model, this enables trusted advisory built on governance, measurable outcomes and helping customers act on their risk.”
Security and compliance must be integrated into core infrastructure from day one
 RAJESH MATHKAR
CO-FOUNDER, WYSETEK SYSTEMS TECHNOLOGISTS PVT. LTD.
"At Wysetek, we have transitioned from traditional perimeter defenses to a proactive, multi-layered Zero Trust Architecture (ZTA) and Secure Access Service Edge (SASE) to secure the borderless enterprise. Our acquisition of Scalezee allows us to embed DevSecOps directly into cloud-native application modernization, ensuring robust security and compliance are integrated into our clients’ core infrastructure from day one.
To combat AI-driven threats such as deepfakes, identity fraud and advanced social engineering, our Next- Gen Cyber Defense Centre (CDC) relies on continuous User and Entity Behavioural Analysis (UEBA), AI- driven anomaly detection, Dark Web and Brand Monitoring, comprehensive Threat Intelligence hunting and custom phishing simulations. Through our monthly Security Threat Advisory (STA) newsletter, we continuously educate customers on emerging cyber risks, newly discovered vulnerabilities, active threat campaigns and recommended mitigation actions, helping organizations stay ahead of evolving threats and strengthen their security posture proactively. This proactive approach enables customers to identify and mitigate emerging threats before they impact business operations. We empower our 400+ certified technology experts to operate as true consultants through an outcome-based framework centred on business resilience and regulatory compliance. Our teams guide enterprise leaders through comprehensive threat landscape evaluations, custom risk assessments and rigorous IT security audits. CyberAdvisor—our AI-powered pre-sales assistant—helps customers quickly explore our Managed Security Services (MSSP) and product solutions, while our experts design the complex architectures, enabling customers to make faster, more informed decisions."
Security must be built with resilience as a design principle, not as an afterthought
 RAJVEER SHAH
GLOBAL CHIEF STRATEGY OFFICER, MITSUMI DISTRIBUTION
“Cybersecurity is a core pillar of Mitsumi's distribution strategy, and the nature of the threat landscape has shifted in ways that demand a fundamentally different approach. AI-driven attacks, whether through deepfakes, identity fraud, or sophisticated social engineering, are no longer edge cases. They are active, scalable, and increasingly difficult to detect using conventional security frameworks. Our response has been to move beyond distributing point solutions and focus on helping our partners embed security at the architectural level. This means working with our vendors to ensure that solutions reaching end customers are built with resilience as a design principle, not as an afterthought. Across our footprint, we carry a portfolio of cybersecurity solutions that includes AI-native capabilities spanning threat detection, identity protection, and infrastructure hardening. Our direction is clear: as AI-powered threats grow in sophistication, the solutions our partners deploy must grow with them. We are actively building that roadmap in close alignment with our vendor ecosystem, with an eye toward making AI-driven security a defining pillar of how Mitsumi goes to market. Equally important is the human layer. Through structured, vendor-led training programmes, we are equipping our partner community with the knowledge to move beyond product sales and engage customers as genuine security advisors. In an environment where customers are prioritising strategic risk management over transactional purchasing, that advisory capability is what differentiates a trusted partner from
a commodity reseller. At Mitsumi, our mission is to ensure our partners are always on the right side of that distinction.”
Protection Must Be Designed into the Foundation, Not Bolted on Later
 RAUNAK JAGASIA
DIRECTOR, SAVEX TECHNOLOGIES PVT. LTD.
“Security used to assume attacks were rare and needed a master hacker, so a strong wall kept most people out. AI has shattered that myth. Today, a teenager in a garage can strike like a seasoned pro because AI hands over years of skill and technique on day one. Picture AI letting a gully cricketer bat like Virat Kohli in his very first match, having absorbed a lifetime of practice overnight. When anyone can attack at expert level, a taller wall isn’t enough—protection has to be designed into the foundation, not bolted on later.
AI has made scams cheap, convincing and personal. Think of the calls many of us now get—a parcel in your name has been found with drugs, or your number will be disconnected over an unpaid bill—designed to create panic so you hand over money or an OTP. With AI cloning voices and faking official identities, these traps look more genuine than ever. We help partners deliver layered defence that verifies who’s really calling, reads behaviour and flags what doesn’t add up before the panic does its damage.
Customers no longer want a catalogue of products—they want someone who understands their risk. So we turn partner teams into advisors, not order-takers. Think of Munna Bhai: the doctor everyone trusts isn’t the one reading out the report, but the one who treats the whole patient and tells you what’s really wrong. We train partners on frameworks, compliance and real AI-security scenarios so they can hold board-level conversations about risk. The distributor that wins this decade won’t move the most product—it’ll build the most trusted advisors.”
AI-driven threats require AI-driven defense and a secure-by-design approach
 RENU VARMA
DIRECTOR, SATCOM INFOTECH PVT. LTD.
“The cybersecurity conversation has evolved from perimeter defense to organizational resilience. As a Value-Added Distributor, Satcom Infotech helps partners and customers adopt a secure-by-design approach by integrating security across endpoints, networks, identities, data and cloud environments. Through solution architecture, technical enablement and cybersecurity training, we enable our ecosystem to build security into infrastructure from the outset rather than treating it as an afterthought. Our focus is on helping organizations create resilient, scalable and future-ready security frameworks that can adapt to an increasingly complex threat landscape. AI-driven threats require AI-driven defense. We work closely with leading cybersecurity technology providers that leverage advanced threat intelligence, behavioral analytics, identity protection and AI-powered detection capabilities to identify emerging risks. We also focus on awareness, partner readiness and proactive security assessments that help organizations recognize and respond to sophisticated attacks before they disrupt operations. By combining advanced security technologies with continuous monitoring and risk-based security strategies, we help organizations strengthen their defences against deepfakes, identity fraud and AI-powered social engineering campaigns. Customers today expect guidance, not just products. We continuously invest in technical certifications, cybersecurity training programmes and solution-focused enablement to help our teams understand evolving threat landscapes and business challenges. By combining technology expertise with a consultative approach, we empower our teams to help partners and customers align cybersecurity investments with long-term resilience, compliance requirements and business objectives while delivering measurable value.
Countering AI-driven threats requires an integrated multi-OEM security architecture
 SAI GOPAL
DIRECTOR, SOFTCELL TECHNOLOGIES GLOBAL PVT. LTD.
“In customer conversations, the attacker side has clearly moved faster on AI. Phishing is cheaper to run, voice cloning has become trivial, and fake mandate calls into finance are an everyday risk. The defender side is catching up, mostly through AI built into the OEM platforms customers already use. Most customers ask the same question: can their existing stack and team absorb this pace, and where to add capability without overspending. That is where Softcell steps in as the integrator.
Most customer estates we work with still have a strong perimeter focus, and that is not wrong; the perimeter still matters. But the bigger investments are now in identity, data protection and behaviour monitoring. As a multi-OEM integrator, we assess the estate, identify real gaps, and recommend additions across our partner stack. A typical engagement today involves three or four OEMs working together, where earlier one perimeter vendor was often enough.
The key concerns we hear are deepfakes in financial fraud, voice cloning of senior executives, and compromised credentials traded online. The defensive capability sits inside OEM platforms, and our role is to combine them effectively—AI-based email security from one OEM, identity protection from another, and behavioural analytics from a third—so they work together in the customer environment. Our consultants bring production experience across environments, supported by continuous OEM certification across the security stack and our status as a CERT-In empanelled Information Security Auditor Organisation.”
Turning core infrastructure into an inherently secure asset through AI collaboration
 SANJAY PATODIA
CEO & DIRECTOR, GALAXY OFFICE AUTOMATION PVT. LTD.
“At Galaxy, we have evolved from providing traditional perimeter firewalls to embedding "secure-by- design" resilience directly into our customers' core infrastructure. By integrating Zero Trust, cloud security, identity management, and automation into every layer, we shift the focus from merely blocking threats to ensuring organizations can securely operate, withstand attacks, and recover instantly. The engine driving this transformation is the collaboration between Galaxy’s AI team and Cybersecurity experts. Together, they co-develop tailored solutions that combine predictive AI threat intelligence with deep human expertise, turning infrastructure into an inherently secure asset. Galaxy has developed Protaigo, an AI-powered solution built to proactively neutralize AI-driven threats before they disrupt business operations. Leveraging machine learning and behavioral analytics, Protaigo delivers real-time detection, automated risk assessment, and intelligent response to combat sophisticated risks like deepfakes, identity fraud, business email compromise (BEC), and advanced social engineering. This solution is co-engineered through the collaboration of Galaxy’s AI team and Cybersecurity experts, fusing data science with security expertise to significantly reduce fraud and build intrinsic resilience. As customers prioritize strategic risk management over product-centric purchasing, Galaxy is positioned as a trusted advisor through its tightly integrated AI & Cybersecurity teams. This collaboration enables business-focused, advisory conversations rather than traditional, product-led sales. By combining cybersecurity knowledge with insights into AI risks, governance, compliance, and cyber resilience, our experts translate high-level business risks into tailored, resilient solutions that protect enterprises and build long-term immunity against evolving threats.”
Resilience over pure prevention is driving our secure-by-design approach
 SATISH KUMAR
DIRECTOR - CONSULTING & SERVICES, DIGITALTRACK SOLUTIONS PVT. LTD.
“Classic cybersecurity was largely about perimeter defence, but this model has been eroding for more than 15 years with remote work, cloud adoption, and evolving security concepts such as Zero Trust and Security Mesh. At the same time, attackers are leveraging AI and an expanding attack surface, making a secure-by-design approach essential within the core infrastructure and development life cycle, rather than layering security on top. We emphasise and educate our clients on Zero Trust by default, Infrastructure as Code, and Policy as Code, helping them build immutable infrastructure with AI-driven defence mechanisms focused on resilience over pure prevention.
Security is in Digitaltrack’s DNA, and we have strengthened our security posture to address emerging
AI-driven threats. Our approach combines behavioural analytics, anomaly detection, and UEBA to identify AI-enhanced phishing and social engineering, along with deepfake detection through media forensics, liveness checks, and content authentication. We also focus on identity protection using biometric AI, continuous verification, and fraud scoring, supported by automated response platforms that counter AI-generated threats in real time. Our sales teams, field advisors, and professional services workforce are trained in AI security consulting, cyber resilience programmes, and strategic risk management. Through training, enablement, and platform-centric advice, we help customers consolidate tools, adopt Zero Trust and secure-by-design, and use behavioural AI against deepfakes, prompt injection, and model attacks. By shifting from product demos to business risk discussions, ROI modelling, exposure management, and broader resilience strategies, we are increasingly seen as trusted advisors rather than transactional partners.”
We are replacing the assumption of internal trust with Zero Trust
 VAIBHAV CHAUDHARI
CHIEF INFORMATION & TECHNOLOGY SECURITY OFFICER, ESSEN VISION SOFTWARE PVT. LTD.
“The transition involves shifting from ‘castle-and-moat’ perimeter defence, where firewalls block threats from entering but trust the inside, to a Secure by Design model. We deploy micro- mentation, treating every server, cloud workload, and Operational Technology (OT) environment as its own isolated zone. We are replacing the assumption of internal trust with Zero Trust, embedding security into the core infrastructure rather than layering it on top.
Rather than relying purely on signatures, we use modern security platforms that utilise forensic science combined with machine learning models to detect microscopic anomalies. Modern Identity and Access Management (IAM) architectures demand active liveness verification, requiring users to perform random, non-static physical actions to prove personhood, while systems continuously evaluate user behaviour instead of checking credentials only at login. Secure email and collaboration gateways leverage Natural Language Processing (NLP) to parse the semantic intent and subtle emotional cues of incoming messages. Threat intelligence telemetry feeds data into an autonomous Security Operations Center (SOC), triggering automated playbook responses that instantly revoke credentials, isolate affected endpoints, and update the global security mesh across hybrid networks in real time. As customers increasingly prioritise strategic risk management over product-centric purchasing, we are shifting metrics from product sales to risk reduction. Our teams undergo mandatory upskilling in AI governance and compliance, conduct framework-driven consultations, and co-design incident response and business continuity with customers, strengthening AI security and cyber resilience.”
Moving from cybersecurity as a product to cyber resilience as a business strategy
 ZAKIR HUSSAIN RANGWALA
CEO, BD SOFTWARE DISTRIBUTION PVT. LTD.
“At BD Software Distribution, we have evolved from distributing traditional firewall and perimeter security solutions to enabling a holistic cyber resilience strategy for our partners and customers. Today’s threat landscape requires security to be embedded across the entire IT ecosystem rather than deployed as standalone products. We help organisations adopt a secure-by-design approach through advanced endpoint protection, XDR, identity security, cloud security, email protection, backup and recovery, security awareness, and compliance-focused solutions, helping customers proactively reduce risk, strengthen business continuity, and build resilience from the outset of their digital transformation initiatives.
The rise of AI-powered attacks has significantly changed the cybersecurity landscape. We address these challenges through advanced security solutions that leverage AI-driven threat detection, behavioral analytics, XDR, MDR, identity protection, email security, and phishing prevention technologies. These solutions help detect and mitigate deepfakes, identity fraud, business email compromise, and social engineering attacks before they impact business operations. We also educate partners and customers through awareness programmes, training workshops, and cybersecurity best practices to strengthen both technological defences and human awareness against emerging AI-enabled threats. As cybersecurity conversations shift from products to business risk and resilience, we are investing in training, certifications, and knowledge development for our teams and channel partners. By combining technical expertise with an understanding of business challenges, we help customers improve their security posture and build long-term resilience. Our vision is to help organisations move from cybersecurity as a product to cyber resilience as a business strategy, enabling them to operate securely in an increasingly AI-driven, digital-first world.”
Security is no longer a standalone product but an architectural layer
 ZUHAIR HUSAIN
DIRECTOR, PENTACLE IT SOLUTIONS PVT. LTD.
“At Pentacle IT Solutions, we have evolved from deploying perimeter-centric security solutions to building cyber resilience frameworks integrated into our customers’ digital transformation journeys. As a Sophos Gold Partner in Uttar Pradesh, we focus on a secure-by-design approach that combines next-generation firewalls, endpoint protection, identity security, network segmentation, continuous monitoring, and proactive risk assessments. Security is no longer treated as a standalone product but as an architectural layer embedded across infrastructure, applications, users, and data from the very beginning.
The rise of AI-powered cyberattacks has significantly changed the threat landscape. To address this, we leverage AI-assisted threat intelligence, Sophos MDR/XDR capabilities, behavioural analytics, and automated incident response mechanisms to identify emerging threats before they impact operations. We are also helping customers prepare against deepfake-enabled fraud, credential compromise, phishing, and social engineering attacks through user awareness programmes, identity-centric security controls, and continuous threat monitoring. Our focus is on reducing attack surfaces while improving detection and response speed. Customers today seek strategic guidance rather than product recommendations. We invest heavily in technical certifications, cybersecurity workshops, and consultative engagement models that align security initiatives with business objectives. By combining industry expertise, AI-driven security insights, and long-term risk management strategies, we enable organisations to strengthen cyber resilience, accelerate digital adoption, and confidently navigate an increasingly AI-driven threat environment, acting as trusted advisors throughout their cybersecurity journey.”