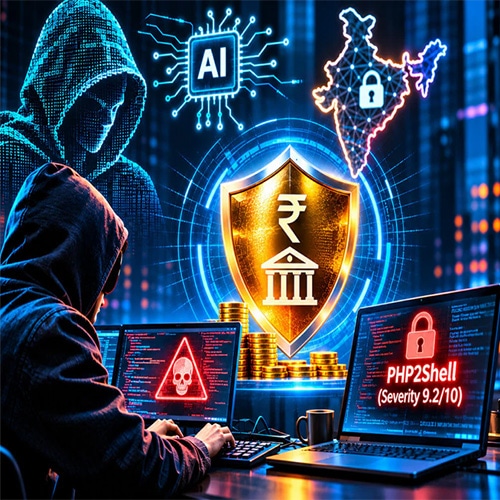
CERT-In warns that cybercriminals are weaponising four AI-driven hacking tools to automate attacks, exploit payment APIs and execute fraudulent financial transactions at machine speed.
India's financial sector is facing a new generation of cyberattacks as Crafty Falcon, an AI-assisted threat actor identified by CERT-In, targets non-banking financial companies (NBFCs), fintech platforms, digital lenders, payment aggregators and cryptocurrency exchanges.
In its November 4, 2026 advisory, CERT-In warned that the campaign remains active, with attackers exploiting financial institutions' own payment and disbursement APIs to initiate unauthorised transactions. The group has reportedly targeted organisations again after incomplete security remediation.
Four AI Tools Behind the Attacks
CERT-In identified four publicly available offensive security tools associated with the campaign:
-
ARTEX: An LLM-powered offensive security framework supporting automated penetration-testing activities.
-
PentAGI: An autonomous multi-agent system capable of coordinating security-testing tasks and adapting attack strategies.
-
Cairn: An attack search engine that helps identify potential weaknesses and attack opportunities.
-
CyberStrikeAI: An AI-assisted offensive security framework that supports automated attack workflows and script generation.
Together, these technologies allow attackers to discover vulnerabilities, generate customised scripts, adapt their methods and execute attacks at machine speed.
How Crafty Falcon Targets NBFCs
The campaign frequently exploits exposed testing and staging environments, subsequently moving into production systems through shared credentials, tokens or network connections.
Attackers also abuse cloud management services, reverse-engineer applications and manipulate API requests to bypass conventional security controls.
One particularly alarming technique involves initiating ₹1 test transactions to validate unauthorised payment routes before attempting larger fund transfers.
CERT-In also observed attacks during weekends and holidays, when reduced security monitoring can delay detection.
The Bigger Threat: Agentic AI Meets Financial Fraud
Crafty Falcon represents a significant shift from conventional hacking towards AI-assisted, adaptive cybercrime.
Instead of manually developing individual exploits, attackers can use autonomous tools to continuously test weaknesses, modify attack scripts and coordinate multiple activities.
This creates a dangerous imbalance: while financial institutions rely on human-led investigation and response, attackers increasingly operate at machine speed.
Why Traditional Cybersecurity Is No Longer Enough
CERT-In has recommended continuous monitoring, stronger API authentication, separation of testing and production environments, rapid vulnerability remediation and automated threat containment.
Financial institutions must also monitor suspicious low-value transactions, enforce server-side payment validation and detect unusual AI-tool activity within their infrastructure.
The central challenge is no longer simply preventing unauthorised access. It is ensuring that every digital identity, API request and financial transaction is continuously verified.
The Road Ahead
Crafty Falcon demonstrates how AI-powered cybercrime is evolving from data theft into automated financial exploitation.
For India's NBFCs and fintech ecosystem, the response must combine zero-trust security, intelligent fraud detection, behavioural analytics, transaction monitoring and automated incident response.
The next cybersecurity battle will be fought between autonomous attackers and intelligent defenders. Financial institutions must ensure their security systems can detect and respond at the same speed as the threats they face.