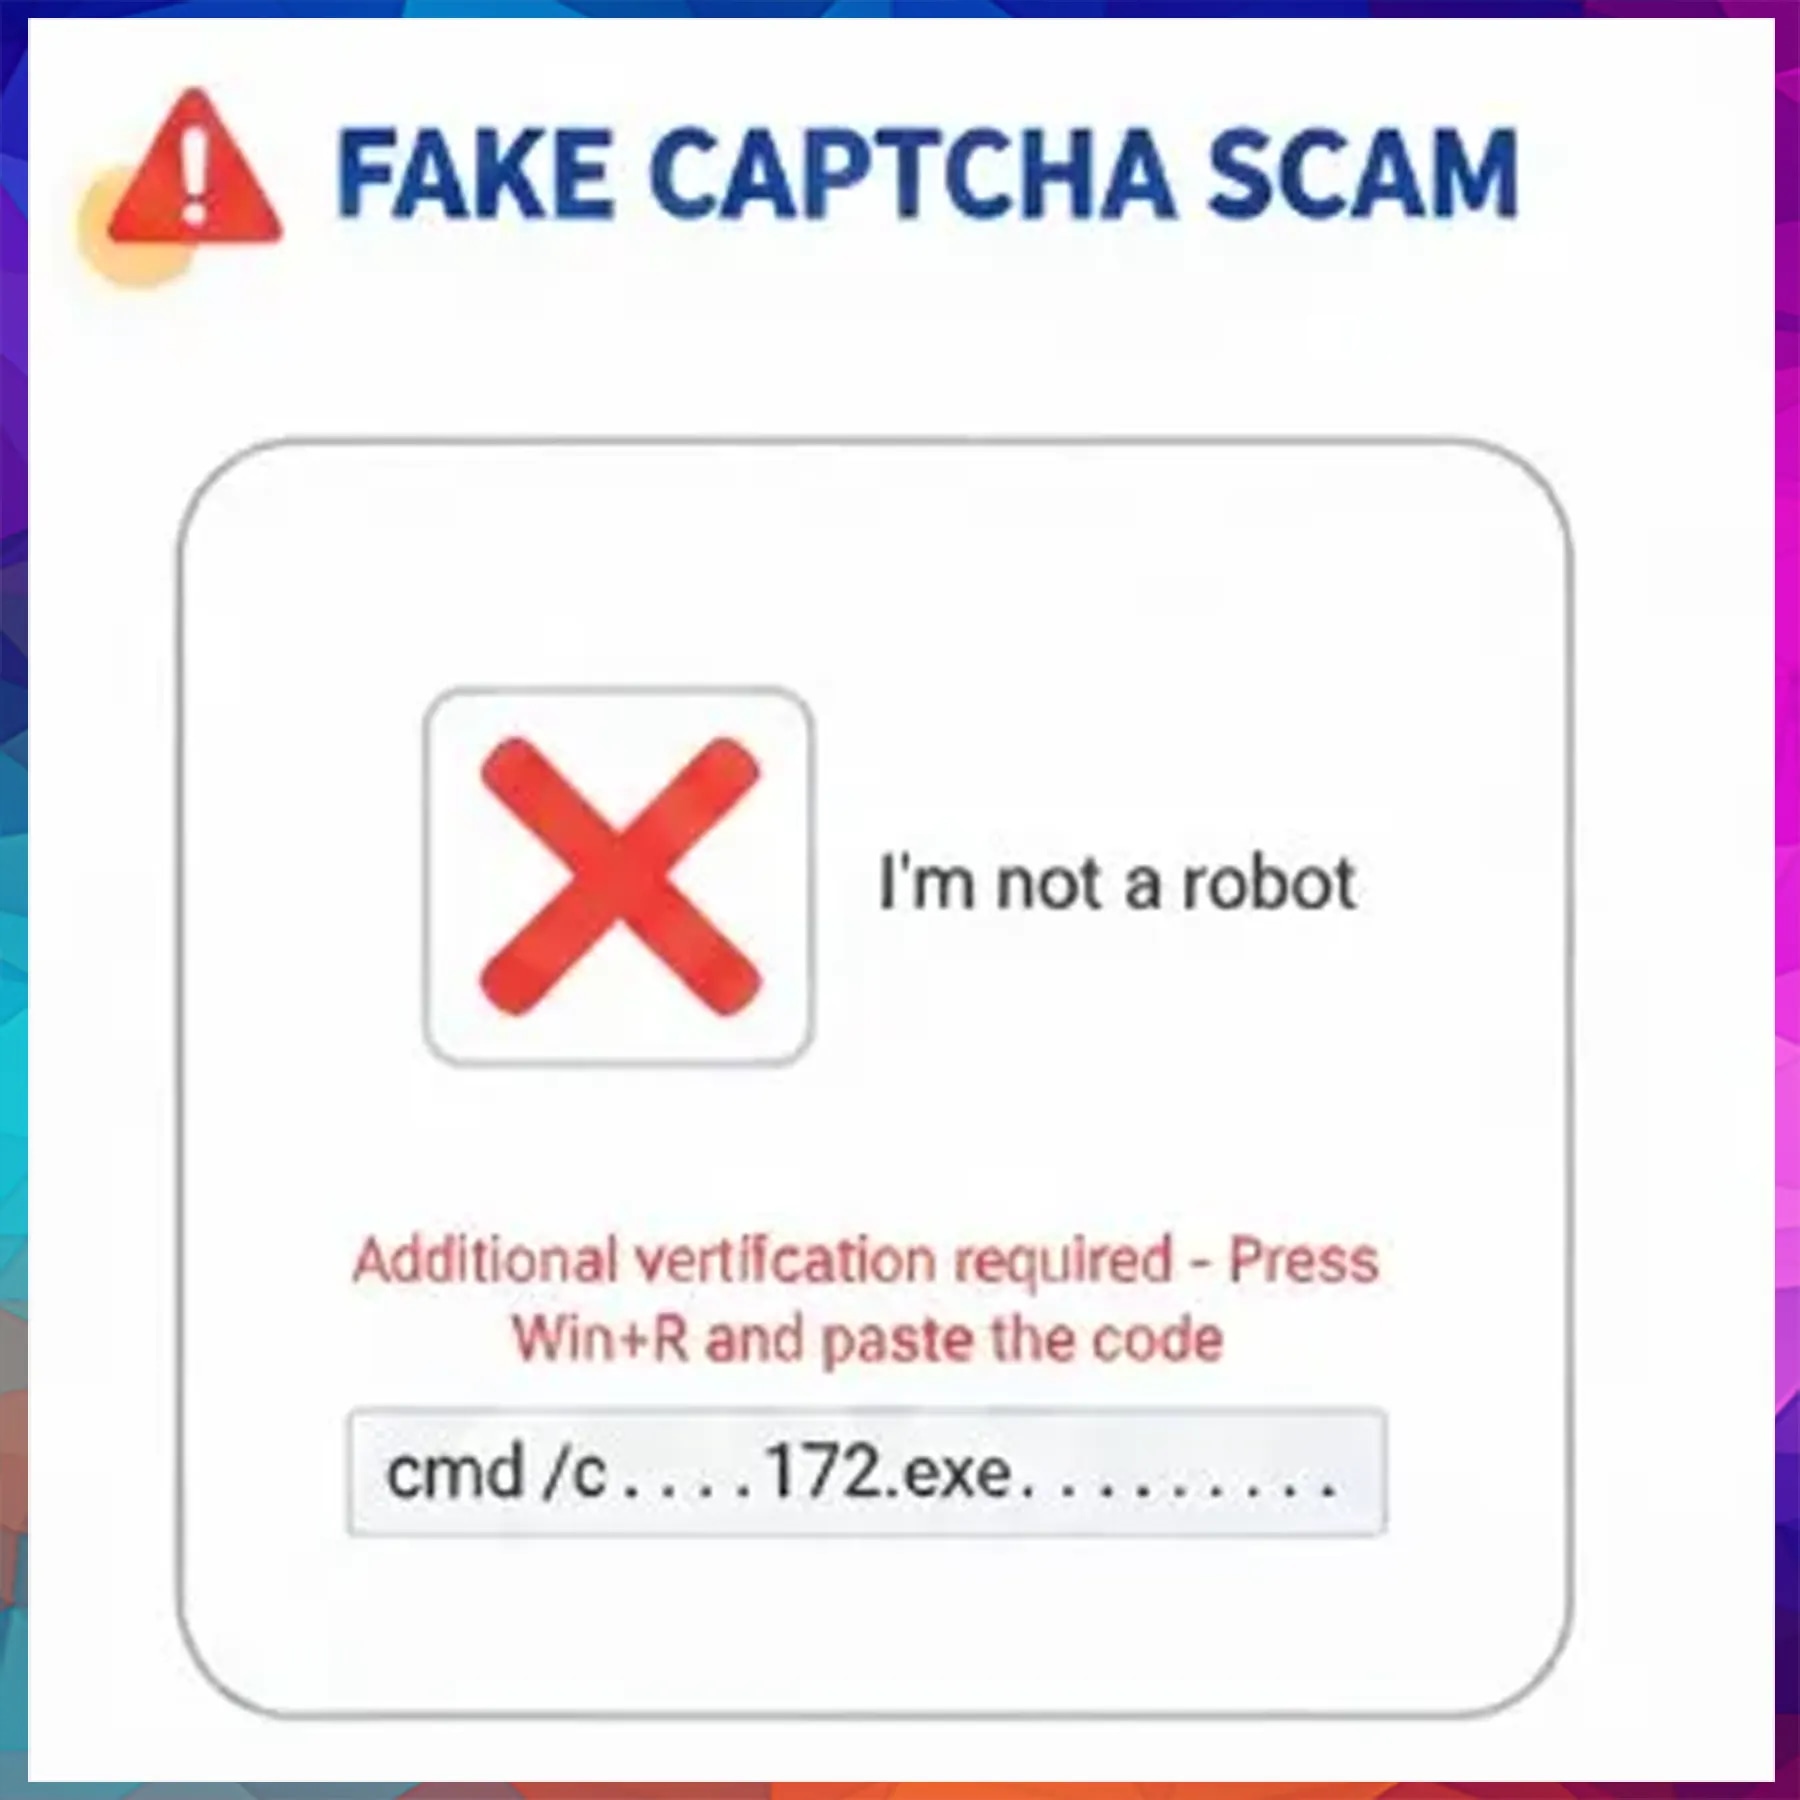
Microsoft says that a command ran on more than 1.1 million unique devices between February and early May 2026, displaying a fake CAPTCHA asking users to press Windows+R, then Ctrl+V, then Enter, and close the tab. Those three keys don’t prove anything but the trick is called ClickFix. It’s behind the r/OutOfTheLoop thread “what’s going on with websites asking people to press Windows+R”.
ClickFix skips the usual warning signs and the user ends up installing a malware.
Windows+R opens the Run box, a small Windows window that launches whatever program or command you type into it. Ctrl+V pastes. Enter runs it, with the same access to your files and accounts that you have.
On clicking the fake “I’m not a robot” button, code on the page quietly copies a command to the clipboard. Microsoft Threat Intelligence described this in an August 2025 analysis.
In one campaign, “clicking the button copied the malicious code on the user’s clipboard in the background.” The on-screen “verification steps” just walk you through pasting and running it.
The keystrokes vary. The University of Münster’s May 2026 warning lists Win+X followed by “i”, which opens Windows Terminal. Microsoft’s new report describes a “FileFix” version that uses the File Explorer address bar instead.
One rule covers all of them. As the Federal Trade Commission put it in a June 8 consumer alert, “Real CAPTCHAs won’t ask you to run commands on your device.” A real one asks you to tick a box, read squiggly letters or pick out traffic lights.