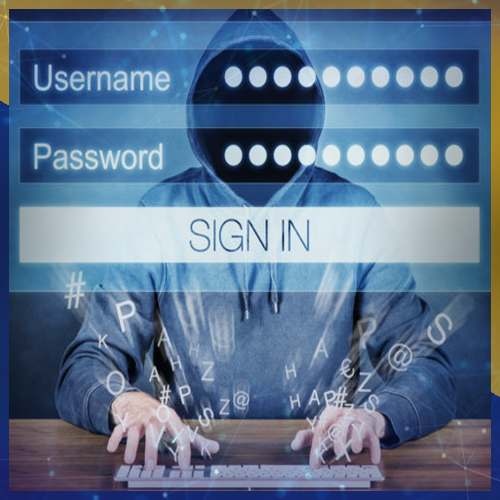
According to a report, the new string of the REvil ransomware has now been adapted by the group Sodinokibi to now encrypt the files on computer while at the same time also change victim’s Windows 10 login passwords.
The new string changes the login passwords and puts the system into the Safe Mode, where only core Windows system services are allowed to run. Regular safety mechanisms like anti-virus software or any user deployed data protection methods are not functional in Safe Mode. Taking advantage of this limited functionality the malware carries out its encryption process unhindered before the user is able to reboot the machine.
The report also claims that the new re-worked string of the REvil ransomware automates the rebooting process, by changing the user password to “DTrump4ever.” This basically eliminates the process for the malware to wait for the user to manually reboot into the safe mode, thus guaranteeing that the PC will be compromised using this method.
It is unknown if new sample strings of the REvil ransomware continue to use the DTrump4ever password or not. Along with this, Sodinokibi has also announced that they will be performing DDoS attacks on victims and email victims’ business partners about stolen data if a ransom is not paid.