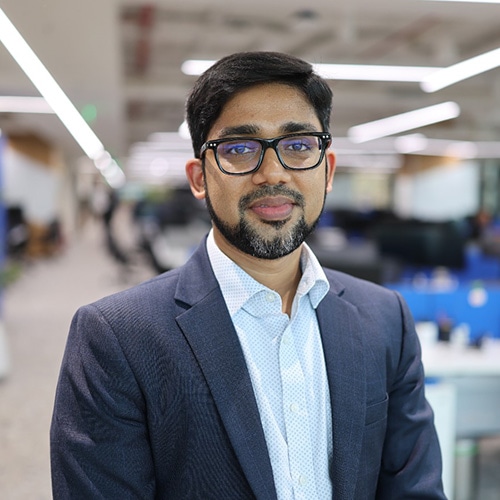
Abdullah Zubair, VP – Technology at BCE Global Tech, explains how enterprises can use AI to strengthen cyber defence while controlling what autonomous agents can access, which actions they can take and how those decisions are audited.
AI can help security teams detect unusual activity and investigate threats faster. But as enterprises give autonomous agents access to proprietary data and production workflows, those agents become part of the infrastructure that security teams must protect, says Abdullah Zubair.
“As AI agents are granted access to proprietary data, production workflows, and decision-making pipelines, they effectively become privileged non-human identities,” Zubair says. “While AI accelerates our defensive posture, enabling machine-speed anomaly detection, automated triage, and predictive threat hunting at scale, it simultaneously expands the attack surface.”
How can enterprises secure the agents they deploy?
Zubair says excessive permissions can allow a compromise to spread across systems, while malicious instructions inserted into a prompt can hijack an agent. He calls for controls that limit what agents can access and do during operation.
“To prevent catastrophic lateral movement or prompt-injected hijackings, security teams must enforce strict least-privilege access, dynamic runtime guardrails, and human-in-the-loop authorization for high-impact actions,” he says.
How does governance support data protection and compliance?
For Zubair, compliance calls for ongoing oversight. “Organizations must continuously prove where sensitive data resides, which models or agents can access it, and how decisions are generated. Our architecture embeds governance directly into the AI lifecycle.”
He describes BCE Global Tech’s approach as combining fine-grained, context-aware access controls, end-to-end data lineage and immutable audit records. He says these controls are designed to prevent sensitive data exposure through prompts and application programming interfaces, while helping organisations demonstrate how data is accessed and used.
What does effective protection look like?
“Ultimately, effective cybersecurity is defined by risk reduction, not tool count,” Zubair says. “Legacy security stacks create friction and alert fatigue; our platform unifies telemetry, identity governance, and runtime protection without operational bloat.”
He points to two ways enterprises can limit the impact of a potential incident: continuously mapping the paths through which an exposure could spread and restricting excessive permissions before they can be exploited.
“Security must be the brakes that allow the business to drive faster,” Zubair says.