Canonical published new Linux kernel security updates for all supported Ubuntu releases to address several vulnerabilities, including the infamous “Dirty Pipe” vulnerability.
This vulnerability only affects Ubuntu 21.10 and Ubuntu 20.04 LTS systems running the Linux 5.13 kernel and could allow a local attacker to modify any file that could be opened for reading.
For all supported Ubuntu releases, the new security update patches three Spectre-related flaws, CVE-2022-0001, CVE-2022-0002, and CVE-2022-23960 that could allow a local attacker to expose sensitive information due to insufficient hardware mitigations added by ARM and Intel to their processors to address the Spectre-BTI vulnerabilities.
The new kernel security update also patches CVE-2022-25636 that could allow a local attacker to cause a denial of service or possibly execute arbitrary code, also for all supported Ubuntu releases.
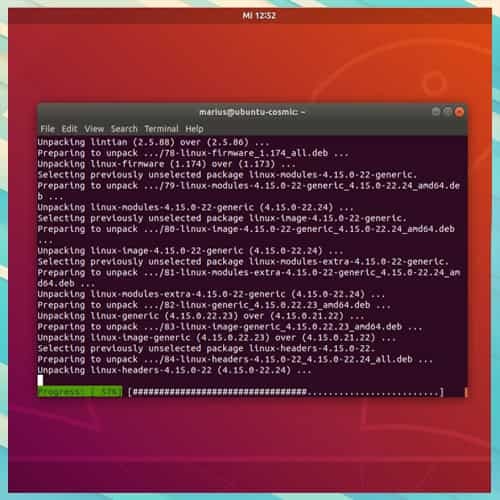
Canonical urges all Ubuntu users to update their installations to the new Linux kernel versions available in the stable repositories (linux-image 5.13.0.35.44 for Ubuntu 21.10 and Ubuntu 20.04.4 LTS, linux-image 5.4.0.104.108 for Ubuntu 20.04 LTS, as well as linux-image-hwe 5.4.0.104.118~18.04.89 for Ubuntu 18.04.6 LTS).
To update your installations, use the Software Updater utility to install all available updates or run the ‘sudo apt update && sudo apt full-upgrade’ command in the Terminal app. Please keep in mind to reboot your installations, as well as to rebuild and reinstall any third-party kernel modules you might have installed after applying the new kernel security patches.