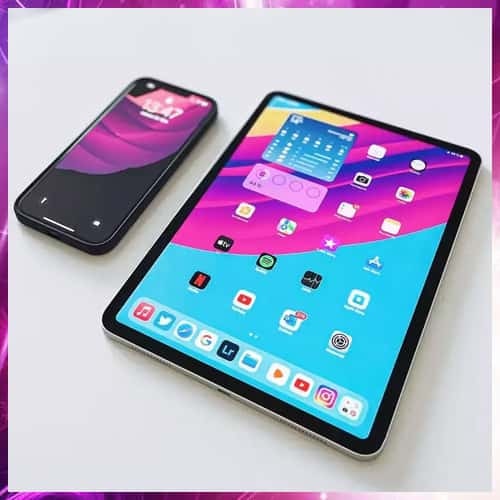
The Indian Computer Emergency Response Team (CERT-In) has issued an advisory about multiple vulnerabilities reported in Apple iOS and iPadOS which could allow a remote tracker to access private data, run arbitrary code, spoof the interface address, or cause a denial of service on the targeted device.
According to reports, the vulnerability affects Apple iOS 16.1, Apple iOS versions previous to 16.0.3, and iPadOS versions prior to 16, along with Apple iPhone 8 and after, iPad Pro Call models, iPad Air 3rd generation and later.
Some of the reasons why vulnerabilities exist in Apple iOS and iPadOS include:
· Improper security restrictions in AppleMobileFileIntegrity component
· Improper bounds check in Avevideoencoder component; Improper validation in CrNetwork component
· Improper entitlement in Core Bluetooth component
· Improper memory handling in GPU Drivers component
· Memory corruption issue in the IOHIDFamily component
· Improper security restrictions and Improper path validation in the Sandbox component
· Improper UI handling, Type confusion and Logic issues in the Webkit component
In its note, CERT-In said, “A remote attacker could exploit these vulnerabilities by persuading the victim to open a specially crafted file or application. Successful exploitation of these vulnerabilities could allow the attacker to gain access to sensitive information, execute arbitrary code, spoofing of the interface address, or denial of service conditions on the targeted system.”
On the same day, the watchdog also reported multiple vulnerabilities in Apple Safari versions prior to 16.1. Users are advised to apply appropriate software updates. The vulnerability exists due to inadequate security controls in the AppleMobileFileIntegrity component among a slew of other factors.