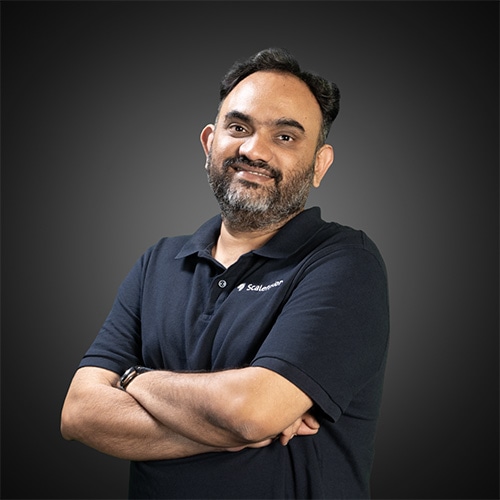
Sriram Kakarala, Chief Product Officer, Scalefusion
Zero trust and context-aware access are central to measurable security
“I think the biggest cybersecurity challenge in an AI-powered enterprise right now is that trust has become extremely fragile. Just because an app or a device worked safely yesterday does not automatically grant it implicit trust to be safe today.
Data security is only as strong as our understanding of the context in which data is accessed, used and secured. And in an enterprise, that context rarely stays the same. That understanding is central to how we've built Scalefusion.
Through UEM, Veltar and OneIdP, we bring endpoint management, security, identity and access together through a single centralized dashboard, grounded in a Zero Trust approach. The idea is to connect what has traditionally been treated as separate security decisions: whether a device can be trusted, whether a user should have access, and what happens when either of those conditions changes.
For me, the real test of security isn't simply whether a policy exists, but whether an enterprise can enforce it consistently, adapt it as risks evolve, and demonstrate that it's working. That's particularly important as data privacy and regulatory expectations continue to change.
I think what sets us apart is that we don't treat security as a collection of alerts from disconnected tools. At Scalefusion, device posture shapes access decisions. A compliance gap triggers a fix. The security controls travel with the endpoint, regardless of where the work happens. The benefit is that it keeps security measurable.
Enterprises should be able to track compliance posture, unresolved vulnerabilities, remediation time and access-policy violations. As AI makes threats faster and harder to predict, the advantage comes from shrinking the time between detecting exposure and actually removing it.”