The Ministry of Electronics and Information Technology (MeitY) has reinforced the importance of timely implementation of India's Digital Personal Data Protection (DPDP) framework, calling upon organisations to begin preparing their data governance, privacy and compliance systems without delay.
Addressing the DPDP Act Readiness Workshop in New Delhi, Shri S. Krishnan, Secretary, MeitY, emphasised that implementing the DPDP Act is a collective responsibility involving government institutions, businesses, technology providers and other stakeholders.
He urged organisations to undertake a comprehensive review of their existing personal data, contractual arrangements, internal processes and operational practices from a data protection compliance perspective. Such assessments would help identify potential gaps and establish a structured roadmap towards regulatory readiness.
Krishnan also highlighted the forthcoming constitution of the Data Protection Board of India, which will play an important role in the country's data protection regulatory framework. He reminded stakeholders of the prescribed compliance timelines, reinforcing the need for organisations to initiate preparations proactively rather than wait until deadlines approach.
The Secretary appreciated the National Informatics Centre (NIC) for developing assessment frameworks and digital tools intended to accelerate DPDP readiness. These initiatives are expected to help stakeholders evaluate their preparedness, identify compliance requirements and strengthen their data protection practices.
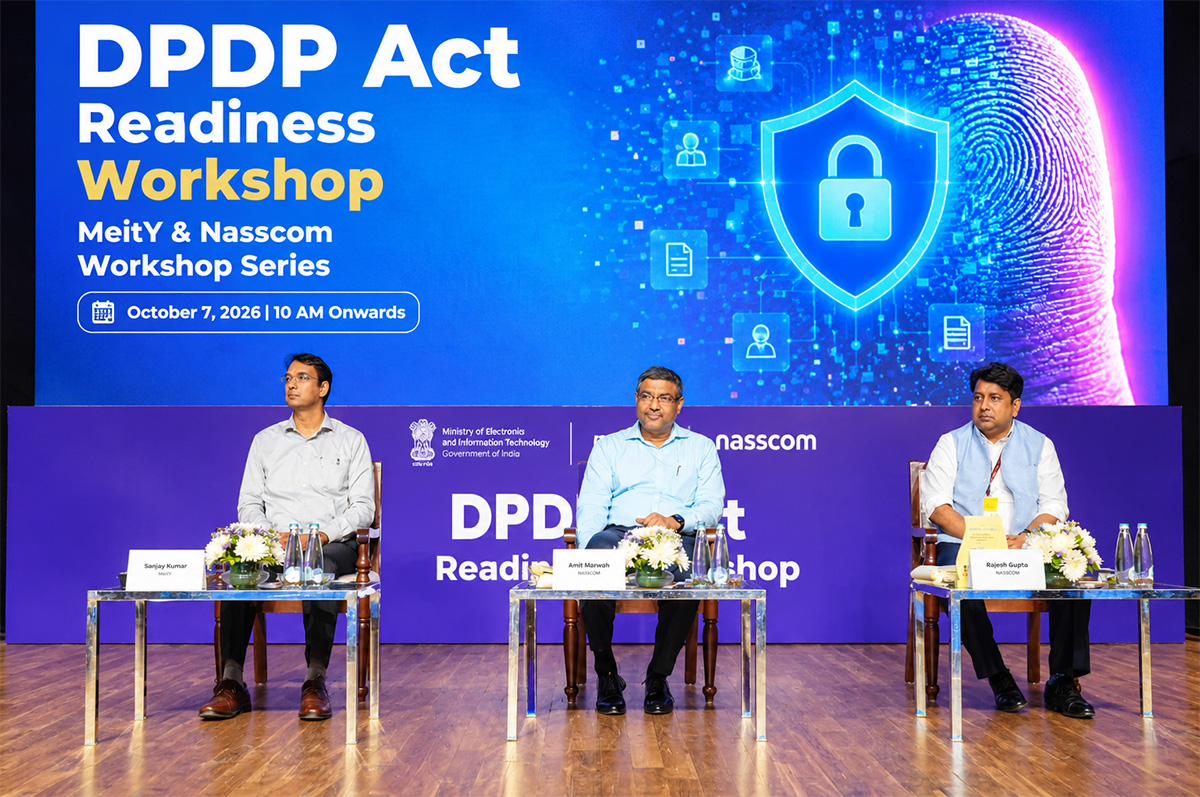
The workshop's message comes at a critical stage in India's privacy transition. According to the National e-Governance Division, the DPDP Rules, 2025 were notified in November 2025, with key Data Fiduciary obligations scheduled to take effect by 13 May 2027. The October 7 readiness workshop brought together stakeholders to examine practical implementation challenges across business-to-business, consumer-facing and government environments.
For enterprises, banks, technology companies and government departments, compliance preparation must extend beyond drafting privacy policies. Organisations need to assess data inventories, consent mechanisms, third-party contracts, security safeguards, data retention, breach response and accountability structures. NIC's broader capacity-building initiatives have also highlighted privacy-by-design, data minimisation and responsible data sharing.
The larger message is clear: DPDP compliance must become an operational priority, not a last-minute regulatory exercise.Organisations that begin reviewing their data ecosystems, strengthening governance and implementing appropriate privacy controls now will be better positioned to meet their obligations while building greater trust among customers and citizens.