India and Indonesia recorded the highest share of surveyed businesses reporting phishing incidents at 28% each, while 70% of respondents in India said their organisations had faced attacks that exploited employees’ low IT security awareness.
Nearly one in four businesses surveyed across Asia Pacific (APAC) reported experiencing phishing between March 2025 and March 2026, making it the most frequently reported cyber incident in Kaspersky’s regional survey. The share stood at 24% across APAC, with Malaysia also above the regional average at 26%.
Respondents ranked phishing as the second most dangerous external cyber threat, behind attacks that exploit vulnerabilities in software and systems.
Attackers target corporate and customer data
Among APAC respondents whose organisations experienced cyber incidents, 33% said attackers sought sensitive business information, such as financial credentials and legal documents, during their most harmful incident. Another 32% identified customers’ personal information as a target.
Respondents also reported disruptions to websites, online stores and critical business operations, along with financial losses. In Vietnam, 39% of respondents whose organisations experienced cyber incidents reported disruptions to customer-facing services during their most harmful incident, compared with 24% across APAC.
Employee awareness remains a concern
Across APAC, 63% of respondents said their organisations had experienced at least one cyberattack that exploited employees’ low IT security awareness. Vietnam recorded the highest share at 75%, followed by India and Malaysia at 70% each.
The survey also found that 55% of APAC respondents rated their organisation’s cybersecurity culture as average, meaning employees knew some basic IT security practices but applied them inconsistently. That share rose to 71% in Vietnam and 62% in Thailand.
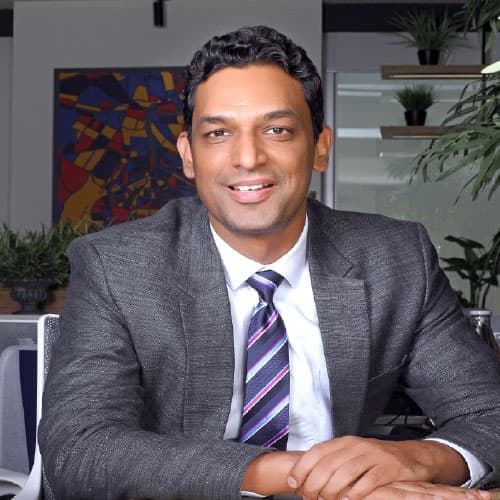
“A phishing email can look like any other message on a busy workday, from a supplier's invoice to a request from a colleague. Employees may know what phishing is, but recognising it in everyday communications can be a challenge. Businesses need to move beyond teaching employees what to look out for and give them opportunities to practise identifying suspicious requests through simulated phishing attacks, while reinforcing those skills over time. The real measure is not whether employees have completed training, but whether they can recognise a threat before acting on it,” said Adrian Hia, Managing Director for Asia Pacific at Kaspersky.
Kaspersky calls for stronger verification and reporting
Kaspersky recommends verifying unusual payment requests, changes to bank details and requests for confidential information through a separate, trusted channel. It also advises businesses to run regular phishing simulations and make it easy for employees to report suspicious messages, including cases where they have already clicked a link.
The company recommends pairing those measures with email security tools that detect malicious links and attachments, regular software updates and multi-factor authentication to help prevent unauthorised access if credentials are compromised.