A newly discovered Android vulnerability named Pixnapping lets malicious apps steal sensitive on screen data—like 2FA codes, messages, and financial details—without needing any permissions.
Researchers demonstrated the Pixnapping attack on Google Pixel (6 through 9) and Samsung Galaxy S25 devices running Android 13–16.
The technique exploits a hardware-level side channel called GPU.zip, along with Android APIs, to extract individual pixels from other apps or websites.
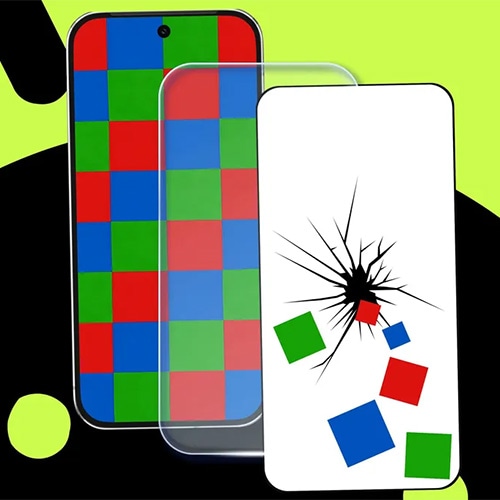
Here’s how it works: a malicious app invokes a target app (e.g. Google Authenticator) so that sensitive data gets rendered.
Then it applies graphical operations to specific pixel coordinates and uses timing differences in rendering to infer the pixel values (white vs non-white).
By repeating this pixel-by-pixel, it reconstructs the original content—such as a 2FA code—in under 30 seconds.
Because the calls used are read-only and produce no blockchain-like transaction or system log, the attack remains stealthy.
Also, the malicious app does not require any declared Android permissions, making detection harder.
Google has rated Pixnapping a High Severity issue under CVE 2025 48561 and issued initial patches.
However, researchers say workarounds still exist, and fixing it fully will likely require changes to core Android rendering mechanisms.
Users should apply updates immediately, avoid installing untrusted apps, and monitor device security bulletins to stay protected.