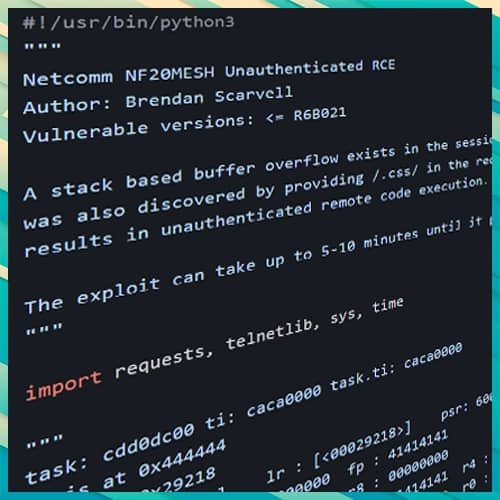
A researcher has found security vulnerabilities in Netcomm and TP-Link routers, some of which could be exploited to achieve remote code execution. The two vulnerabilities together can permit a remote, unauthenticated attacker to execute arbitrary code.
The attacker can first gain unauthorized access to affected devices, and then use those entry points to gain access to other networks or compromise the availability, integrity, or confidentiality of data being transmitted from the internal network.
Tracked as CVE-2022-4873 and CVE-2022-4874, the flaws concern a case of stack-based buffer overflow and authentication bypass and impact Netcomm router models NF20MESH, NF20, and NL1902 running firmware versions earlier than R6B035.
In an advisory, the CERT Coordination Center (CERT/CC) detailed two unpatched security vulnerabilities affecting TP-Link routers WR710N-V1-151022 and Archer-C5-V2-160201 that could lead to information disclosure (CVE-2022-4499) and remote code execution (CVE-2022-4498).