Global payments giant Visa has confirmed a cybersecurity incident involving a third-party service provider, while a newly emerged ransomware group claims to have compromised both Visa and JPMorgan Chase.
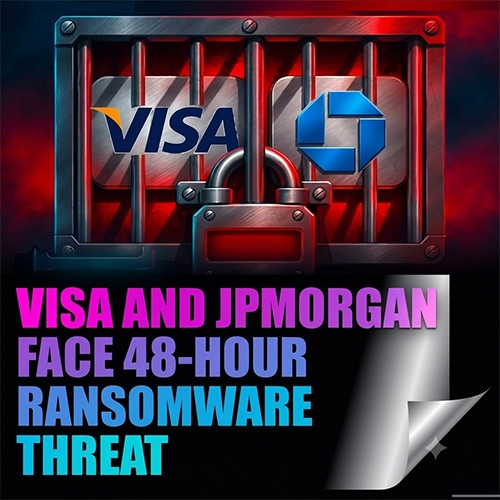
The ransomware group, identifying itself as “non,” has reportedly listed both financial institutions on its victim disclosure platform, threatening to release allegedly stolen information unless negotiations begin within 48 hours.
The attackers have provided limited evidence regarding the nature, volume or sensitivity of the information they claim to possess, leaving the actual extent of the alleged compromises uncertain.
According to Cybernews, the group's claims have raised concerns because both organizations play critical roles in global financial infrastructure, processing transactions and managing sensitive financial information.
Visa has acknowledged the incident but clarified that its own systems were not compromised. The company attributed the exposure to an unidentified third-party service provider operating in the Asia-Pacific region.
A Visa spokesperson stated that the company's systems were neither involved nor affected, adding that there was no indication that payment information, including card numbers, had been compromised.
However, Visa has not publicly identified the affected service provider or disclosed the specific categories of information potentially exposed through the third-party incident.
Meanwhile, the ransomware group's allegations involving JPMorgan Chase remain unverified. No independent technical evidence establishing a successful compromise of the bank was provided in the supplied report.
The incident highlights the growing sophistication of ransomware operations, where cybercriminals increasingly combine data theft, public disclosure threats and aggressive negotiation deadlines to pressure targeted organizations.
Third-party cybersecurity risk has emerged as a major vulnerability for financial institutions, particularly as banks and payment networks depend heavily on external technology providers, cloud platforms and outsourced services.
Even when an organization's core infrastructure remains secure, weaknesses within its vendor ecosystem can expose sensitive business information and create reputational, regulatory and operational challenges.
The alleged 48-hour ultimatum reflects an increasingly aggressive extortion strategy designed to create urgency, attract publicity and potentially force victims into negotiations before investigations establish the facts.
For financial institutions, such threats reinforce the importance of continuous vendor risk assessments, zero-trust architecture, data encryption, privileged access controls and real-time threat intelligence.
Regulators and cybersecurity teams must also strengthen incident reporting, supply-chain visibility and coordinated response mechanisms to prevent isolated vendor compromises from escalating into broader financial-sector disruptions.
The larger warning is clear: cybersecurity resilience extends far beyond an organization's own network. As financial ecosystems become increasingly interconnected, protecting third-party relationships and verifying breach claims are essential to maintaining customer trust and financial stability.