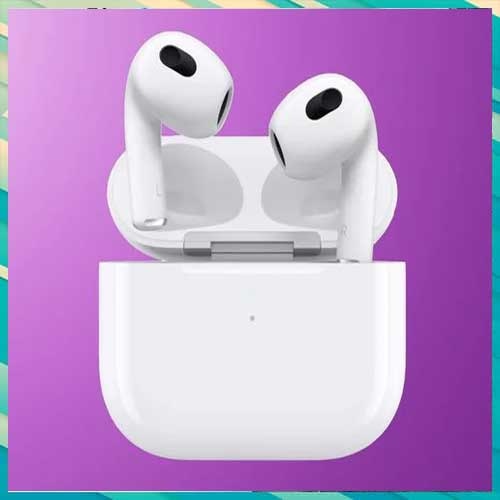
Apple recently updated the firmware on the AirPods, which might make it possible for a malevolent actor to access the headphones without authorization. The authentication problem, which is being tracked as CVE-2024-27867, impacts the following devices: Beats Fit Pro, Powerbeats Pro, AirPods Max, AirPods (2nd generation and later), and AirPods Pro (all models).
"When your headphones are seeking a connection request to one of your previously paired devices, an attacker in Bluetooth range might be able to spoof the intended source device and gain access to your headphones," Apple said in an advisory.
In other words, an adversary in physical proximity could exploit the vulnerability to eavesdrop on private conversations. Apple said the issue has been addressed with improved state management.
Jonas Dreßler has been credited with discovering and reporting the flaw. It has been patched as part of AirPods Firmware Update 6A326, AirPods Firmware Update 6F8, and Beats Firmware Update 6F8. The development comes two weeks after the iPhone maker rolled out updates for visionOS (version 1.2) to close out 21 shortcomings, including seven flaws in the WebKit browser engine.
The vulnerability takes advantage of Apple's failure to apply the permissions model when using the ARKit Quick Look feature to spawn 3D objects in a victim's room. Making matters worse, these animated objects continue to persist even after exiting Safari as they are handled by a separate application.