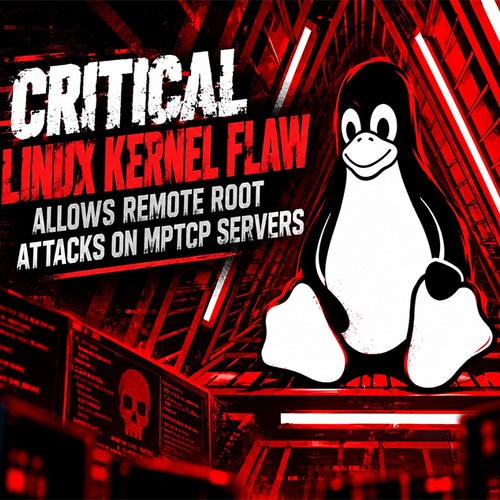
A critical vulnerability in the Linux kernel has raised cybersecurity concerns worldwide, potentially exposing enterprise servers to remote attacks. Identified as CVE-2026-98432, the flaw carries a severity score of 9.8.
The vulnerability affects the kernel's IPv4 TCP connection-handling mechanism and potentially impacts Ubuntu, Red Hat Enterprise Linux and other distributions widely deployed across enterprise and cloud environments.
Security researchers identified a race condition causing a use-after-free vulnerability. Attackers can exploit improper memory handling during TCP connections, potentially triggering crashes, information disclosure or arbitrary code execution.
Anthropic demonstrated an alarming development: its Claude AI model reportedly generated a working exploit capable of obtaining root-level access remotely without authentication on specifically configured Linux servers.
The demonstration highlights how artificial intelligence is transforming vulnerability research. AI-powered systems can accelerate exploit development, potentially narrowing the time available for organisations to implement security patches.
However, severity assessments initially differed. While Linux maintainers assigned a 9.8 rating, vendors issued lower scores based on exploitation complexity and demonstrated impact.
Patch availability has evolved. Debian, Oracle, Amazon Linux and SUSE released fixes for affected versions, while Red Hat subsequently issued updates for RHEL 8, 9 and 10.
Ubuntu has placed fixes for several supported releases into testing channels. Administrators must verify distribution-specific advisories, install appropriate updates and reboot affected systems.
The larger concern extends beyond one vulnerability. AI-assisted exploitation, delayed patch deployment and exposed infrastructure create dangerous opportunities for cybercriminals targeting critical enterprise workloads.
Organisations must strengthen vulnerability management, continuous monitoring and infrastructure resilience. The lesson is clear: AI is accelerating both cyber defence and offensive capabilities, making proactive security essential for digital trust.