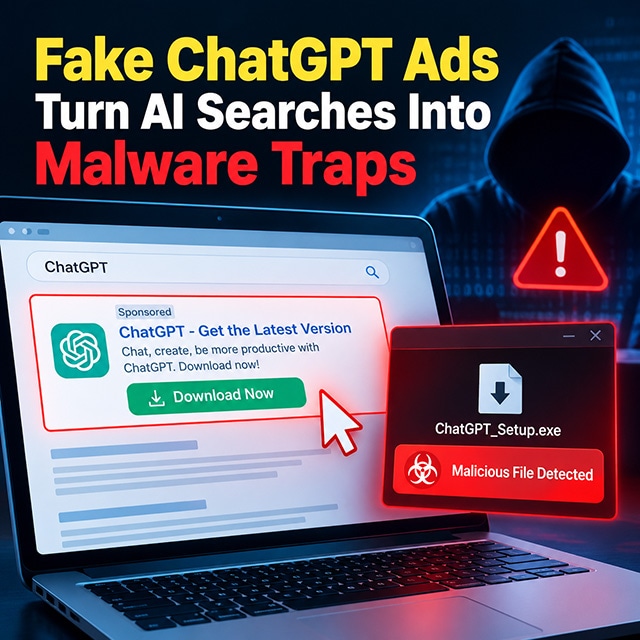
Cybercriminals are exploiting the enormous popularity of ChatGPT by creating convincing advertisements and fake websites designed to trick users into installing malware. What makes the attack particularly dangerous is that the journey can begin with something users normally trust—a sponsored result appearing in Google Search.
The trick is simple. A user searches for ChatGPT or related AI software and sees a professionally presented sponsored advertisement. The branding, wording and website appearance may closely resemble a legitimate service, creating an immediate sense of authenticity.
After clicking the advertisement, however, the victim can be redirected to an imitation ChatGPT page rather than the genuine service. The site may encourage the user to download an application, browser component or other software supposedly required to access the AI service.
That download becomes the real attack. Instead of receiving legitimate AI software, the victim risks installing malicious code capable of compromising the device or exposing sensitive information.
The technique is particularly effective because attackers are exploiting two forms of trust simultaneously: trust in a familiar AI brand and trust in paid search advertisements. Users often assume that sponsored links appearing prominently in search results have already been verified as safe.
This represents an evolution of phishing. Rather than depending entirely on suspicious emails or unsolicited messages, attackers can intercept users while they are actively searching for legitimate technology.
Generative AI has made impersonation even easier. Criminals can rapidly create convincing logos, website content, support messages and interfaces, reducing many of the visual clues traditionally associated with fraudulent websites.
Enterprises face an even greater risk. A compromised employee device can potentially expose corporate credentials, browser sessions, confidential documents and access to enterprise applications, turning one deceptive download into a wider security incident.
The safest approach is to avoid downloading AI applications through advertisements or unfamiliar websites. Users should verify the domain, access software through official sources and treat unexpected installation instructions as suspicious.
The bigger cybersecurity lesson is clear: seeing a trusted brand is no longer proof of trust. In the AI era, organisations must move from assumed trust to continuous verification—validating the source, identity, application and behaviour before granting access to sensitive digital environments.