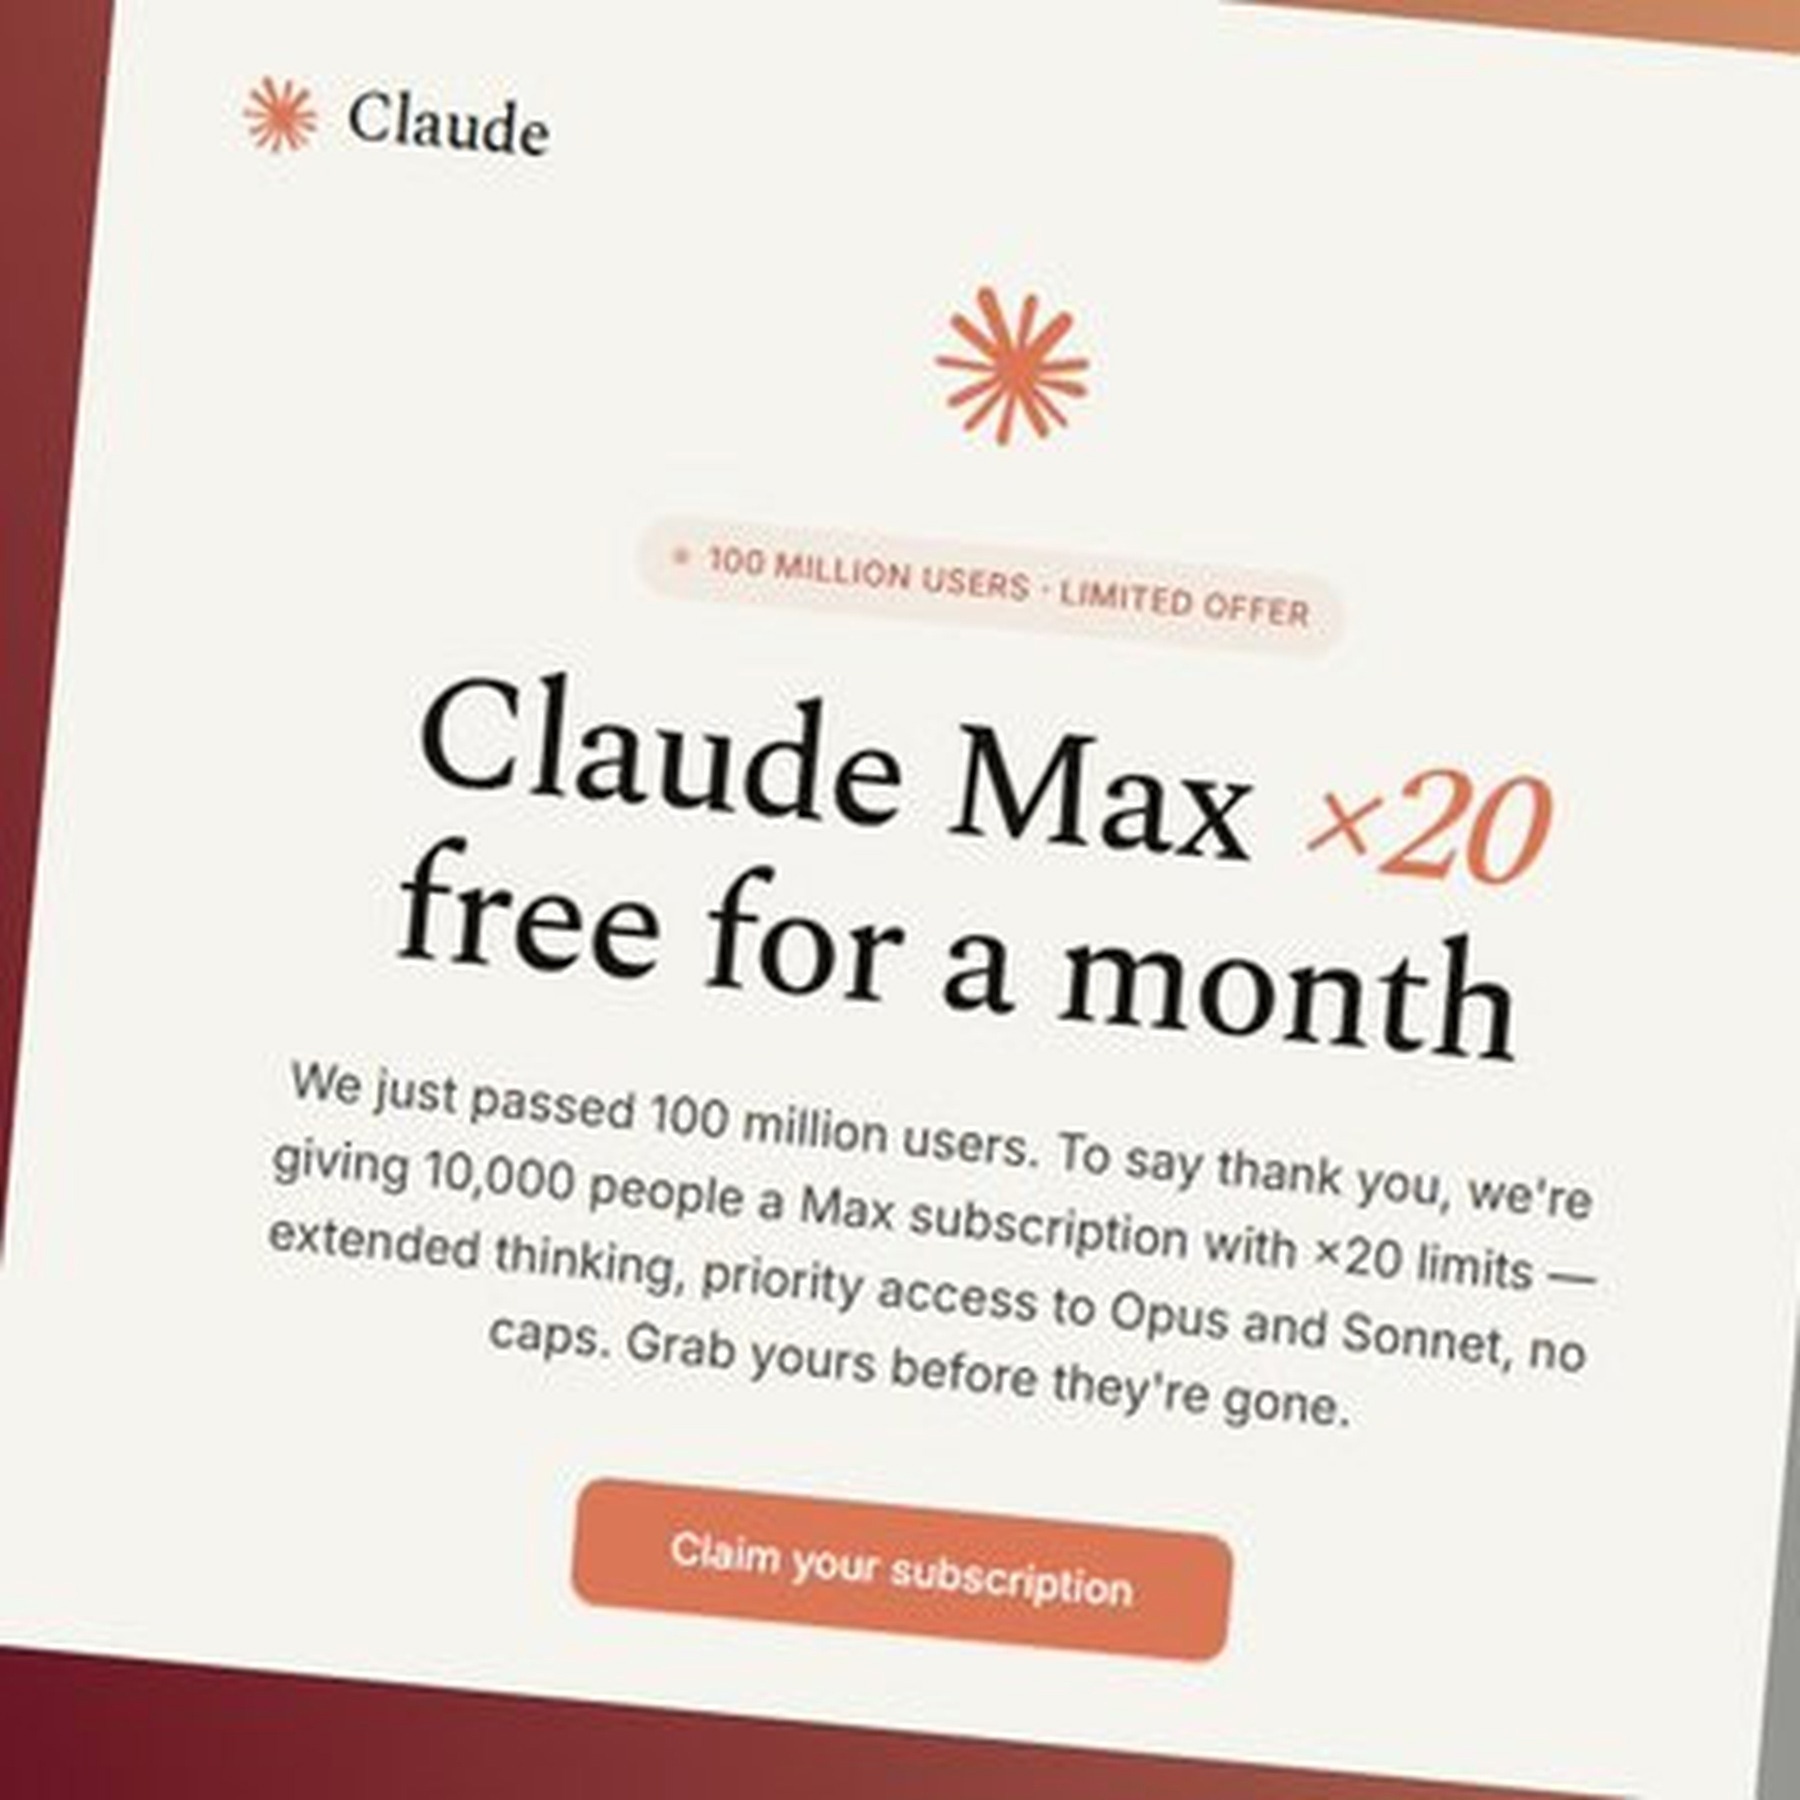
Cybercriminals are exploiting the popularity of premium AI subscriptions with a sophisticated phishing campaign offering a supposedly free Claude Max upgrade. Instead of stealing payment information, the attack targets something potentially more valuable—the victim’s Google account credentials.
The fraudulent website claims Anthropic is celebrating a user milestone by giving away thousands of free Claude Max subscriptions. Authentic-looking branding, fabricated reviews and links to legitimate Anthropic pages make the promotion appear credible, while a countdown showing rapidly disappearing subscriptions creates artificial urgency.
Interestingly, the site repeatedly assures visitors that no payment information is required. Instead, users are encouraged to authenticate using Google. Other login choices are deliberately disabled or redirected, ensuring victims eventually reach the attacker-controlled Google sign-in process.
The most dangerous element is a browser-in-the-browser phishing technique. Rather than opening Google’s genuine authentication page, the website creates a fake browser window inside the existing webpage, complete with a Google address, padlock icon and verification interface.
Because the address bar itself is fabricated, even security-conscious users who normally check URLs can be deceived. The malicious sign-in functionality reportedly comes from reusable external code, demonstrating how sophisticated phishing capabilities can increasingly be packaged and reused across campaigns.
The campaign reflects a broader cybersecurity shift: AI brands are becoming high-value social-engineering bait. Attackers can exploit demand for premium ChatGPT, Claude, Copilot and other AI services to steal credentials that potentially unlock email, cloud documents, password resets and paid AI accounts.
Users should therefore verify promotions directly through official websites, rely on password managers to detect domain mismatches and distrust artificial countdowns. When a popup appears, attempting to move it beyond the webpage can also expose a fake window. As AI services become embedded in everyday work, AI-account phishing is rapidly becoming an identity-security problem, not merely another online scam.