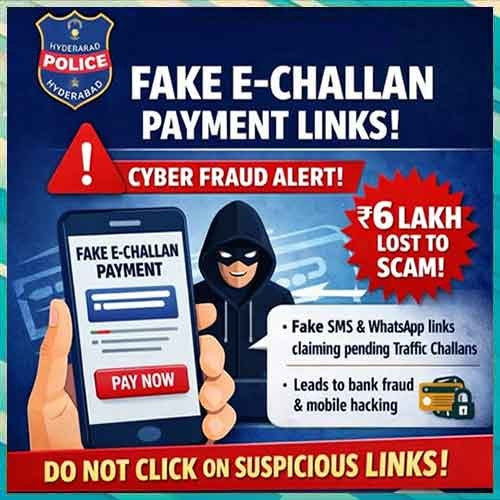
India is witnessing a dangerous rise in cyber frauds linked to fake e-challan payment links, and the trend reflects a deeper shift in how cybercriminals exploit public trust in digital governance. The method used in these frauds follows a predictable but highly effective pattern. A victim receives a message stating that a traffic challan is unpaid and must be settled immediately to avoid penalties or legal action. The message includes a link that appears legitimate — often mimicking government URLs.
Once the link is opened -
· A fake e-challan website loads
· The interface looks identical to official transport portals
· The user is asked to enter vehicle details
· Payment information such as card or UPI is requested
· In many cases, malicious software is silently installed
· Within minutes, money is siphoned from the victim’s account.
What makes this scam particularly dangerous is that nothing looks suspicious at first glance. This is a pattern now being seen repeatedly across urban centres.
The frightening part is that victims often realize what has happened only after receiving bank alerts — by then, the money is already gone.
There are several reasons behind the surge:
- Rapid digitization of government services
- High dependence on mobile payments
- Low awareness of official verification methods
- Blind trust in SMS-based alerts
- Fear of penalties and legal action
People assume that anything related to traffic or government fines must be genuine. Criminals are exploiting this psychological shortcut.