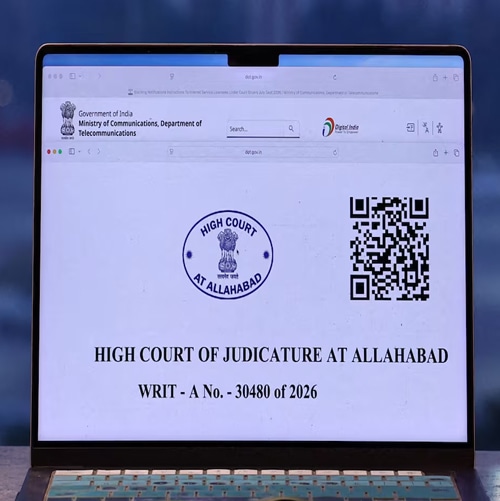
The Prime Minister's Office has reportedly summoned Telecom Secretary Amit Agrawal following concerns over the alleged use of forged court orders, raising questions about verification procedures, administrative accountability, and the security of India's telecommunications regulatory processes.
According to officials cited in media reports, Agrawal was asked to explain the apparent lapse, prompting him to cut short an official visit to another state. The intervention signals the government's concern over the integrity of official documentation.
The controversy highlights a serious governance challenge: how forged judicial documents can potentially influence administrative decisions when authenticity checks are inadequate. Such incidents threaten institutional credibility and expose weaknesses in document verification mechanisms.
Court orders carry significant legal authority, particularly when government departments and telecom operators must act on directions involving communications services, regulatory compliance, or enforcement. Any misuse of judicial documentation could therefore have far-reaching operational consequences.
The reported intervention by the Prime Minister's Office underscores the importance of establishing responsibility and examining whether existing procedures adequately distinguish authentic judicial instructions from fraudulent submissions.
For the telecommunications industry, the episode raises broader concerns about digital trust. As regulatory processes become increasingly electronic, departments must ensure that sensitive instructions originate from verified authorities and pass through secure communication channels.
Cybersecurity experts advocate digitally signed judicial documents, authenticated government communication systems, and independent verification against official court records before implementing consequential orders. These measures can reduce impersonation and document-forgery risks.
Artificial intelligence introduces another dimension, enabling increasingly convincing document manipulation, forged signatures, and institutional impersonation. Traditional visual inspection alone may no longer provide sufficient assurance against sophisticated fraudulent documentation.
The incident also reinforces the need for stronger coordination among judicial institutions, telecommunications authorities, and cybersecurity agencies. Standardized verification protocols, audit trails, and clear escalation procedures could strengthen accountability and prevent similar failures.
The larger lesson is that digital governance requires verifiable trust, not merely digitized paperwork. India's telecommunications ecosystem must prioritize document authenticity, cryptographic verification, and institutional safeguards to ensure that fraudulent instructions cannot undermine lawful decision-making or public confidence.