Mobile applications have become the digital front door to banking, payments, healthcare, shopping, enterprise systems and personal identity. But while users see a familiar interface, attackers increasingly see something very different: APIs, credentials, tokens, device permissions, authentication workflows and valuable data waiting to be exploited.
The biggest problem is that many attacks are effectively invisible to the user—and sometimes even to the organization operating the application.
The Attack Has Moved Beyond Malware
Traditional mobile security concentrated heavily on detecting malicious applications and protecting devices. The modern attack surface is much broader.
Attackers can reverse-engineer applications, manipulate APIs, steal session tokens, abuse legitimate credentials, automate account takeovers, inject malicious code, exploit insecure SDKs and use emulators or compromised devices to imitate legitimate customers.
Generative AI adds another dimension. Fraudsters can increasingly combine deepfake faces, synthetic identities, cloned voices and stolen personal information to challenge onboarding and authentication systems designed for an earlier generation of threats.
The result is an important shift: a legitimate-looking user, device or transaction can no longer automatically be considered trustworthy.
APIs Are Becoming the Hidden Battlefield
Modern mobile applications depend heavily on APIs connecting the interface to cloud infrastructure, payment systems, identity providers and databases.
Attackers do not necessarily need to compromise the application itself. If they discover poorly protected API endpoints, they may attempt credential stuffing, token theft, automated scraping, account enumeration or manipulation of business logic.
This creates an uncomfortable reality: the mobile screen may appear perfectly normal while fraudulent activity is occurring behind it.
Authentication Is No Longer Enough
Passwords, OTPs and even biometric authentication solve only part of the problem.
An attacker who successfully passes the initial authentication layer—or hijacks an authenticated session—may effectively inherit the user's privileges. That makes continuous verification increasingly important.
Security architecture therefore needs to move from: From Authenticate → Trust towards : Authenticate → Observe → Analyse → Continuously Verify → Respond
Behavioural signals such as device changes, unusual navigation, transaction velocity, typing or interaction patterns, beneficiary changes and abnormal session behaviour can provide additional indications of risk.
Third-Party Code Expands the Attack Surface
Few mobile applications are completely self-contained. They frequently incorporate analytics libraries, advertising technology, payment components, authentication services and numerous software development kits.
Every dependency potentially expands the security and privacy boundary.
Organizations therefore need visibility not only into their own source code but also into what third-party components collect, where information travels, which permissions they receive and whether vulnerabilities emerge after deployment.
AI Agents Could Multiply the Risk
The next phase could be even more challenging.
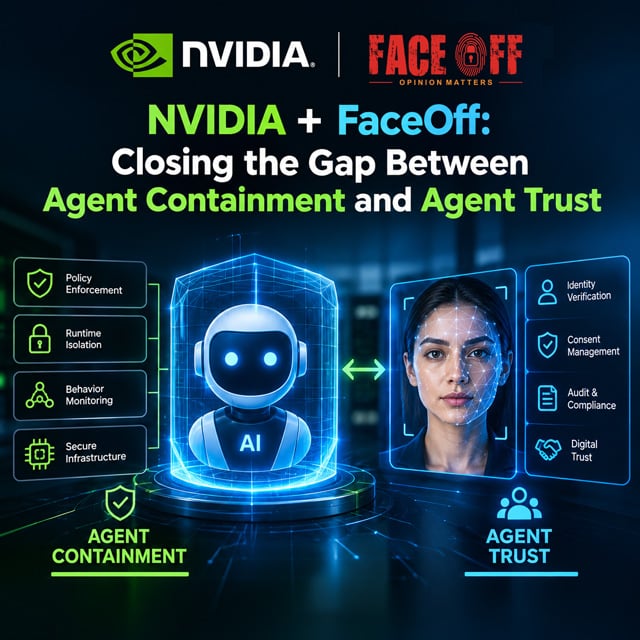
Mobile applications are evolving from interfaces that simply respond to commands into platforms containing AI agents capable of performing actions for users—making purchases, accessing accounts, communicating with services and initiating transactions.
If an autonomous agent is manipulated through prompt injection, compromised credentials, poisoned memory or malicious external content, the attacker may not need to directly control the smartphone. They could potentially manipulate the agent operating on behalf of the user. That changes mobile security from protecting an application to protecting an increasingly autonomous digital identity.
Privacy Is Now Part of Mobile Security
Mobile applications can process location, identity, financial, behavioural, biometric and device information. Consequently, security and privacy can no longer operate as separate disciplines.
India's DPDP compliance environment further increases the importance of knowing what personal data is collected, why it is collected, whether appropriate consent exists, where it is stored and who can access it.
An application can be technically secure while still creating significant privacy exposure through excessive collection, uncontrolled third-party sharing or inadequate governance.
The New Security Model: Never Assume Trust
The future of mobile security will therefore depend less on a single defensive technology and more on continuous risk assessment.
Applications increasingly need to combine device intelligence, application integrity, API protection, identity verification, behavioural analytics, deepfake detection, fraud intelligence, privacy controls and real-time response.
The fundamental question is changing.
Security teams previously asked:
“Has this user successfully authenticated?”
They increasingly need to ask:
“Is the person, device, application, session and behaviour still trustworthy right now?”
That distinction will become critical as mobile applications evolve into gateways for autonomous financial and digital activity.
The most dangerous mobile attack may ultimately be the one that produces no malware warning, no suspicious screen and no obvious breach—because to both the application and the victim, everything initially appears legitimate.