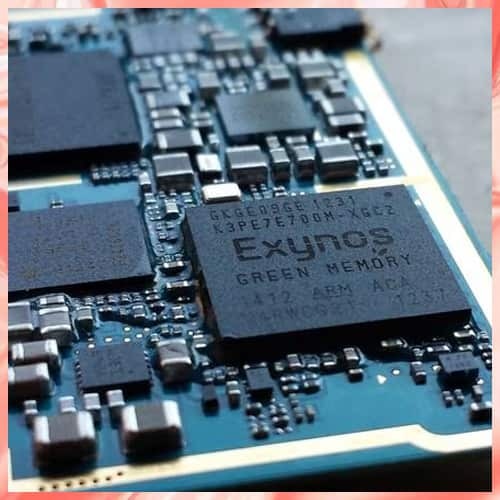
Google's bug-hunting team Project Zero has identified around eighteen security vulnerabilities affecting Exynos modems. A combination of these vulnerabilities that affect Exynos modems can allow a hacker to gain full control and access to a smartphone without the owner of the phone knowing about it. They just need the contact number of the owner of the smartphone. There are a number of devices that can become targets of hacks and attacks, according to Google's Project Zero.
Four of the eighteen vulnerabilities are deemed to be the most critical as they enable remote code execution with just the victim's phone number. Only one of the most serious exploits has a publicly assigned Common Vulnerabilities and Exposures (CVE) number, with Google withholding a number of CVEs associated with this vulnerability in a rare exception to normal bug disclosure protocol.
The following devices are affected, according to Google's Project Zero.
· Mobile devices from Samsung, including those in the S22, M33, M13, M12, A71, A53, A33, A21s, A13, A12 and A04 series;
· Mobile devices from Vivo, including those in the S16, S15, S6, X70, X60 and X30 series;
· The Pixel 6 and Pixel 7 series of devices from Google; and
· Any vehicles that use the Exynos Auto T5123 chipset.
This bug has been fixed in the March security update, which the Pixel 7 series already has. However, the Pixel 6 series does not have it yet, and Google says that users who are using unpatched devices should disable VoLTE and Wi-Fi Calling. As per Project Zero head, a user could have their device compromised and potentially not even know about it, and it seems like it might be pretty easy for some attackers to find and exploit as well.
The other fourteen vulnerabilities (CVE-2023-26072, CVE-2023-26073, CVE-2023-26074, CVE-2023-26075, CVE-2023-26076, and nine others awaiting CVEs) aren't as critical but still carry risk to the end user.