Infostealers Hijack Claude AI Sessions
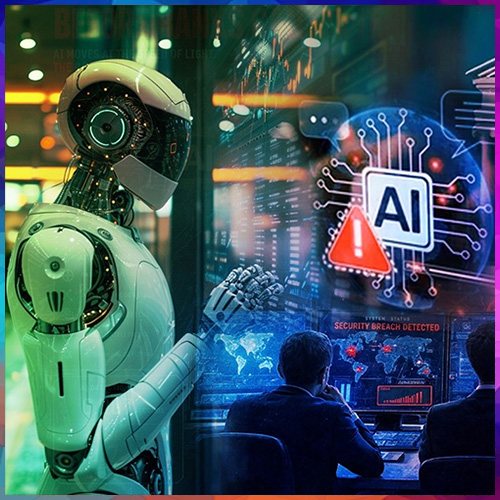
Cybercriminals are reportedly using infostealer malware to hijack Claude accounts, stealing active browser sessions rather than trying to crack passwords or intercept two-factor authentication codes.
According to a warning Anthropic sent to affected users, attackers copied login-session data from infected computers and then used those sessions to access victims’ Claude accounts and consume their usage allowances.
This attack highlights a major authentication weakness: MFA cannot necessarily protect an account when criminals steal a valid authenticated session after the user has already logged in.
For paid subscribers, the financial impact can extend beyond lost usage.
Attackers could potentially consume prepaid usage credits and, where enabled, trigger additional purchases through auto-reload settings.
Anthropic responded by signing affected users out, removing stored payment methods and refunding charges identified as unauthorized.
The company said the malware was not installed through or related to Claude.
Stolen AI accounts could also potentially support phishing, fraud, social engineering and other malicious campaigns.
The incident reinforces an emerging security reality: protecting credentials is no longer enough.
Enterprises need stronger endpoint security, session protection, continuous authentication and behavioural monitoring to detect when a legitimate session changes hands.

See What’s Next in Tech With the Fast Forward Newsletter


Tweets From @varindiamag
Nothing to see here - yet
When they Tweet, their Tweets will show up here.